
Top 10 SOC 2 Type 2 Compliance Service Providers in Saudi Arabia
Quick answer: CyberSapiens is a leading SOC 2 Type 2 compliance service provider for organisations in Saudi Arabia, alongside major audit firms such as EY Saudi Arabia, KPMG Saudi Arabia, and PwC Saudi Arabia. SOC 2 Type 2 certification evaluates how effectively your security controls operate over a defined period, typically six to twelve months, giving Saudi businesses a credible way to demonstrate data protection commitments to regional and international clients.
Introduction to SOC 2 Type 2 compliance
SOC 2 Type 2 is a report that evaluates the design and operating effectiveness of a service organisation’s internal controls over a specific period, typically 6 to 12 months. Unlike a one-time assessment, it proves that controls actually work in practice, not just on paper.
The report is built around five Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. For Saudi businesses serving international clients, especially in technology, finance, and healthcare, SOC 2 Type 2 is increasingly becoming a contractual requirement rather than a nice-to-have.
List of top 10 SOC 2 Type 2 compliance service providers in Saudi Arabia
Here are the top 10 SOC 2 Type 2 compliance service providers in Saudi Arabia, in no particular order.
1. CyberSapiens
CyberSapiens provides all types of SOC compliance, whether SOC 1 or SOC 2 compliance. They follow the best SOC compliance framework and its guidelines to meet client requirements across Saudi Arabia.
CyberSapiens SOC 2 Type 2 Compliance Process
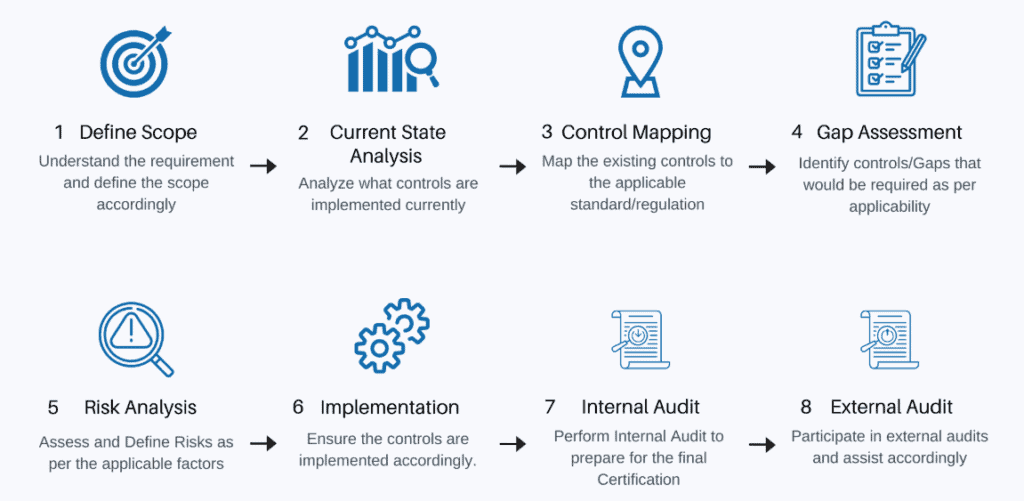
1. Define Scope: Identifies which systems, processes, and services will be included in the SOC 2 review, based on business priorities and customer requirements.
2. Current State Analysis: Evaluates current security controls and operational procedures to determine the existing level of compliance, providing a baseline for improvements.
3. Control Mapping: Compares current controls against the SOC 2 Trust Services Criteria and relevant regulatory standards to identify what already meets expectations.
4. Gap Assessment: Identifies shortcomings, missing controls, or weaknesses that must be implemented or enhanced to satisfy SOC 2 requirements.
5. Risk Analysis: Analyses risks related to security, availability, confidentiality, and other SOC 2 components to prioritise corrective actions.
6. Implementation: Puts necessary controls, policies, and procedures in place, including technical safeguards, documentation, workflows, and employee training.
7. Internal Audit: Carries out an internal evaluation to confirm implemented controls are functioning correctly before the external audit stage.
8. External Audit: A third-party auditor reviews the controls over a defined period for SOC 2 Type II compliance, determining certification.
2. Ernst and Young (EY) Saudi Arabia
Overview: EY Saudi Arabia runs a dedicated cybersecurity and technology risk advisory arm, which typically positions the firm well for SOC 2 readiness work with Saudi fintech and digital-first clients expanding under Vision 2030. Best for enterprises wanting SOC 2 integrated into a broader risk advisory relationship.
3. KPMG Saudi Arabia
Overview: KPMG is one of the Big Four accounting networks with an established presence across the GCC. Its Saudi practice is frequently engaged by public sector and large enterprise clients for governance, risk, and controls assurance work alongside SOC 2 engagements. Best for regulated organisations wanting a globally recognised audit brand.
4. PricewaterhouseCoopers (PwC) Saudi Arabia
Overview: PwC has operated across the Middle East for decades, drawing on PwC’s global network of tens of thousands of assurance professionals. Their scale suits larger Saudi enterprises needing audit and controls assurance alongside SOC 2 readiness.
5. Protiviti Saudi Arabia
Overview: Protiviti is a global risk and internal audit consulting firm rather than a CPA firm itself, so it generally supports SOC 2 readiness, gap analysis, and control design, then coordinates with a licensed CPA firm for the formal attestation. Best for organisations wanting hands-on readiness support before engaging an auditor.
6. RSM Saudi Arabia
Overview: RSM is one of the world’s largest accounting networks, built around mid-market clients. Its Saudi member firm is a common fit for growing businesses wanting an internationally recognised network without Big Four scale and cost.
7. Grant Thornton Saudi Arabia
Overview: Grant Thornton operates as a global mid-market network with a Saudi member firm, generally serving growth-stage and privately-held businesses across assurance, tax, and advisory services. Best for mid-market companies wanting a global network firm with local presence.
8. BDO Saudi Arabia
Overview: BDO is a top-five global accounting network with a mid-market orientation. Its Saudi practice typically serves established SMEs and regional businesses needing assurance services alongside SOC 2 support.
9. Crowe Saudi Arabia
Overview: Crowe is a global accounting and consulting network with a mid-market focus. Its Saudi presence typically serves regional businesses needing assurance and compliance support similar in scale to RSM, BDO, and Grant Thornton.
10. Mazars Saudi Arabia
Overview: Now operating as Forvis Mazars in several markets, this global audit, tax, and advisory network maintains a Saudi presence serving mid-market and multinational clients needing SOC 2 alongside other assurance frameworks.
Benefits of SOC 2 Type 2 compliance
Working with a SOC 2 Type 2 compliance service provider in Saudi Arabia offers several concrete advantages.
1. Enhanced credibility
Demonstrates a verified commitment to security, availability, and data protection to Saudi and international clients alike.
2. Increased customer trust
Provides assurance to customers and stakeholders that an organisation’s internal controls are independently tested, not just documented.
3. Regulatory alignment
SOC 2 controls overlap significantly with Saudi Arabia’s own cybersecurity expectations, including the National Cybersecurity Authority’s Essential Cybersecurity Controls and the Saudi Personal Data Protection Law, making SOC 2 readiness work double as groundwork for local compliance.
4. Competitive advantage
Differentiates an organisation from competitors and strengthens its position when bidding for enterprise and government-adjacent contracts under Vision 2030’s push toward a digital economy.
5. Reduced breach risk and cost
The IBM Cost of a Data Breach Report consistently finds that organisations with mature, tested security controls detect and contain breaches faster and at lower cost than those without, which is exactly what the SOC 2 Type 2 audit period is designed to verify.
Conclusion
SOC 2 Type 2 compliance is essential for Saudi businesses that provide services to customers, particularly in technology, finance, and healthcare, where enterprise buyers increasingly require independent proof of security controls before signing a contract. The providers listed here, from CyberSapiens’ hands-on, end-to-end approach to the Big Four and global mid-market networks, each offer a different mix of scale, specialisation, and pricing. Choosing the right fit depends on the size of your organisation, your industry, and how much hands-on support you need through the readiness process.
CONTENT REVIEWED BY
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
FAQs
What is SOC 2 Type 2 compliance?
SOC 2 Type 2 compliance is a report that evaluates the design and operating effectiveness of a service organisation’s internal controls over a specific period, typically 6 to 12 months, based on the AICPA Trust Services Criteria.
Why is SOC 2 Type 2 compliance important for organisations in Saudi Arabia?
It demonstrates a verified commitment to security, availability, and data protection, which is essential for building trust with customers and stakeholders, and increasingly expected during enterprise and government-adjacent procurement.
What is the difference between SOC 2 Type 1 and SOC 2 Type 2?
SOC 2 Type 1 evaluates the design of an organisation’s internal controls at a single point in time, while SOC 2 Type 2 evaluates both the design and operating effectiveness of those controls over a period of 6 to 12 months.
How long does it take to achieve SOC 2 Type 2 compliance?
The timeline depends on the organisation’s size, complexity, and current readiness, but the audit period itself typically runs 6 to 12 months before a report can be issued.
How much does SOC 2 Type 2 compliance cost?
Cost varies with the size and complexity of the organisation and the services required, and generally ranges from tens of thousands to low hundreds of thousands of Saudi riyal for a full readiness and audit engagement.
How often does an organisation need to renew its SOC 2 Type 2 compliance?
SOC 2 Type 2 compliance is typically renewed annually, since the report reflects control design and operating effectiveness over a specific period, and controls can change over time.
