Posted on October 17th, 2026 by Ketki Tidke
Quick answer: ISO 27001 certification follows nine steps, from setting your scope to passing a two-stage audit by an accredited certification body. This free two-page PDF sets them out for the 2022 edition, with a typical consultant-led engagement alongside. The ISO 27001:2022 Certification Process Many teams start certification without a clear picture of the sequence. […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER Who are the best ISO 27001:2022 service providers in Canada? There is no single best provider, because ISO 27001 services come in two kinds: certification bodies that audit and certify you, and consultants that build your ISMS. Choose one of each and keep them separate, and check the certification body’s accreditation in the […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER What does the ISO 27001 move from 2013 to 2022 mean for your business now? The transition period ended on 31 October 2025, so ISO 27001:2013 certificates are no longer valid. If you transitioned in time, keep your ISMS aligned with the 2022 edition and its 2024 amendment. If you did not, you […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER What is the best ISO 27001:2022 service provider in the UAE? The best choice depends on the job, because the certificate and the preparation come from different types of provider. For the audit and certificate, choose a certification body accredited for ISO/IEC 27001 by the Emirates International Accreditation Centre (EIAC) or another IAF […]
Posted on October 6th, 2026 by Cyber
QUICK ANSWER When to hire a vCISO comes down to one question: is anyone senior accountable for cyber risk at the moment an outside pressure forces the issue? If the answer is no, and a regulator, customer, insurer or board member is asking, it is time to bring one in. The three loudest signs are: […]
Posted on August 4th, 2026 by Cyber
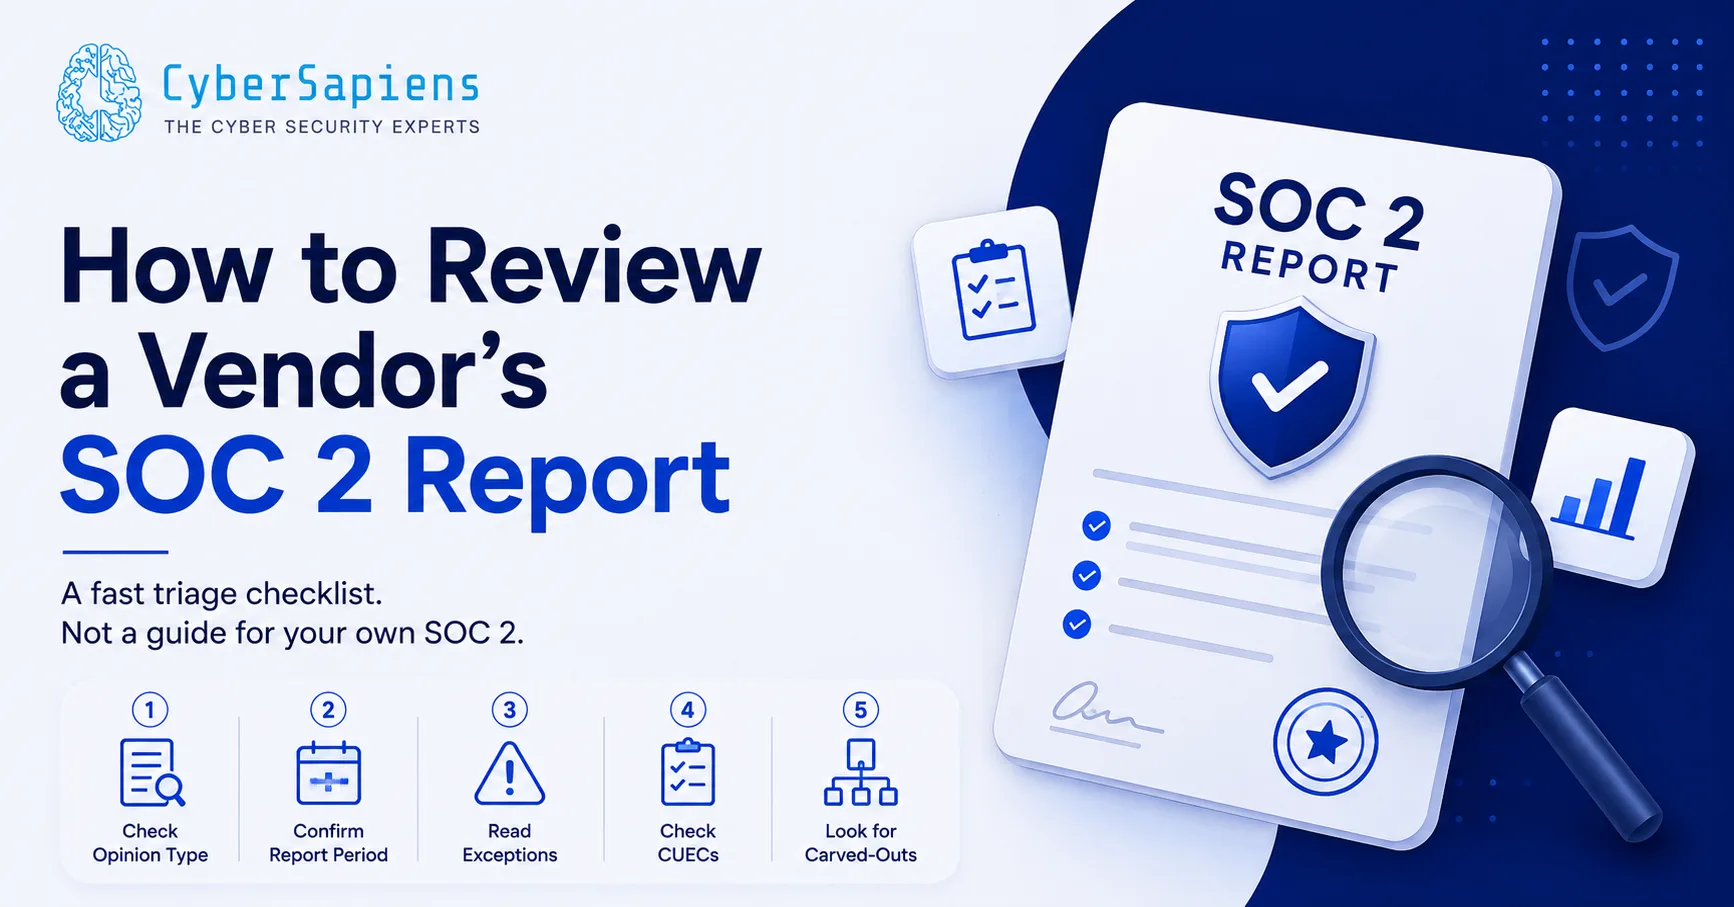
A SOC 2 report can run to 60 or more pages, and most of it is not what you actually need to check. Five things matter most: the auditor’s opinion type, the report period, any exceptions listed, the complementary user entity controls, and whether any subservice organisations are carved out of scope. Check those five […]
Posted on July 31st, 2026 by Cyber
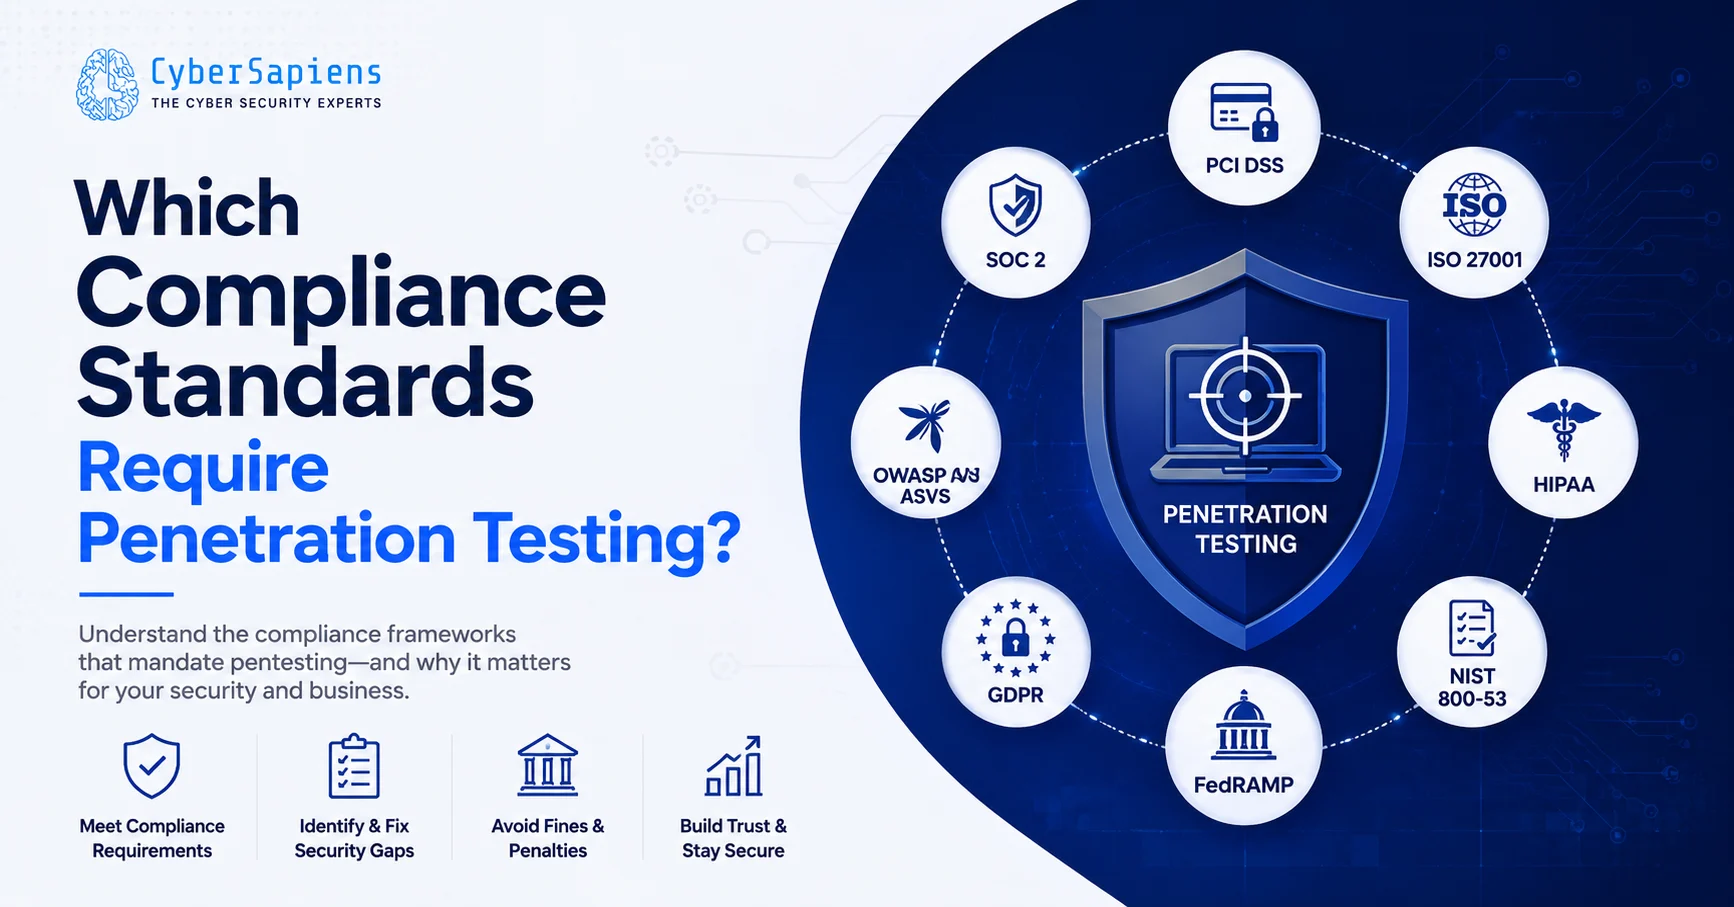
Not every compliance framework treats penetration testing the same way. Some name it explicitly and set a strict schedule. Others imply it through a broader control requirement and leave the frequency to your auditor’s judgement. Knowing which is which before you scope an engagement saves you from either under-testing and failing an audit, or over-testing […]
Posted on July 29th, 2026 by Cyber
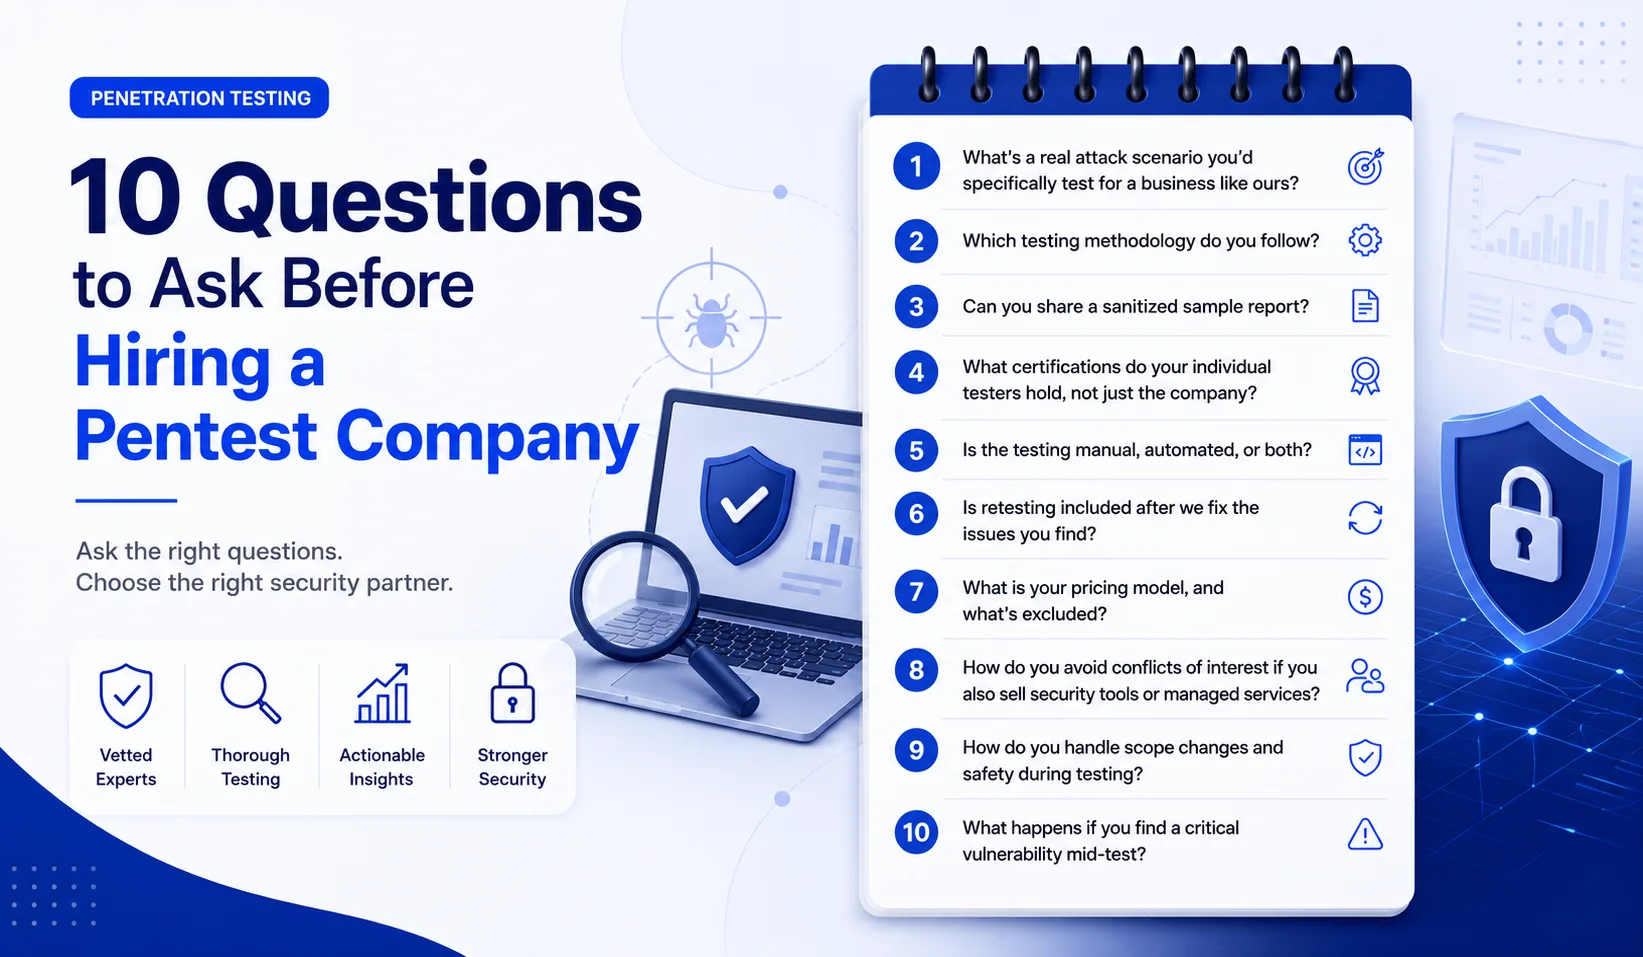
Most penetration testing quotes look identical on paper: a scope, a timeline, a price. The difference between a vendor who finds the vulnerability a real attacker would use and one who hands you a scanner printout with a logo on it only shows up in how they answer questions before you sign anything. Three questions […]
Posted on June 24th, 2026 by Cyber
Australia 2026 Guide Why Security Awareness Training is Essential for Australian Businesses in 2026 Cyber attacks targeting Australian businesses have shifted significantly. Attackers no longer rely primarily on exploiting software vulnerabilities — they increasingly target employees through phishing emails, AI-generated scams, business email compromise, and social engineering campaigns that are becoming harder to detect every […]
Posted on June 23rd, 2026 by Cyber
If your business handles customer data — and in 2026, nearly every US business does — SOC 2 Type 2 compliance is no longer optional. It is the standard that enterprise clients, investors, and government procurement teams demand before signing a contract. SOC 2 Type 2 is an auditing framework developed by the American Institute […]