
SOC 2 and HIPAA Compliance Service Providers in Canada
Quick answer: CyberSapiens is a leading SOC 2 and HIPAA compliance service provider for Canadian businesses, offering tailored readiness assessments, control implementation, and audit coordination. Other established providers include PwC Canada, Deloitte Canada, and KPMG Canada, each varying in scale, pricing, and industry focus.
Data breaches are becoming more frequent and more expensive for Canadian organisations. According to the IBM Cost of a Data Breach Report, the average Canadian breach cost CA$7.11 million in 2026, up from CA$6.98 million the year before, with Canada now ranking among the highest-cost countries globally.
If you are running a SaaS company or handling healthcare data, compliance is no longer optional. SOC 2 and HIPAA compliance service providers in Canada help organisations in Toronto, Vancouver, Montreal, Calgary, and Ottawa put structured controls in place before a breach happens, not after.
What exactly are SOC 2 and HIPAA?
1. SOC 2: your security report card
The American Institute of CPAs built this framework around five areas: Security, Availability, Processing Integrity, Confidentiality, and Privacy.
Most SOC 2 compliance companies in Canada work with tech companies, cloud providers, and managed service providers. Type 1 gives a snapshot in time, while Type 2 proves controls have operated consistently over a period.
2. HIPAA: healthcare’s golden rule
HIPAA is U.S. law, but Canadian companies handling U.S. healthcare data still need to comply with it.
HIPAA compliance consulting in Canada covers the Privacy Rule and Security Rule. These are strict requirements, not suggestions, and non-compliance can end a client relationship or a contract.
Top 4 SOC 2 and HIPAA compliance providers in Canada
1. CyberSapiens: Best SOC 2 and HIPAA Compliance Service Provider in Canada
CyberSapiens does not hand you a checklist and walk away. The process starts with scoping, mapping exactly which systems and processes need coverage under your chosen Trust Services Criteria, then a gap assessment that ranks real risks by what would hurt most if left unfixed.
Trust signal: CyberSapiens holds ISO 27001 certification, demonstrating its own information security management system rather than only auditing others.
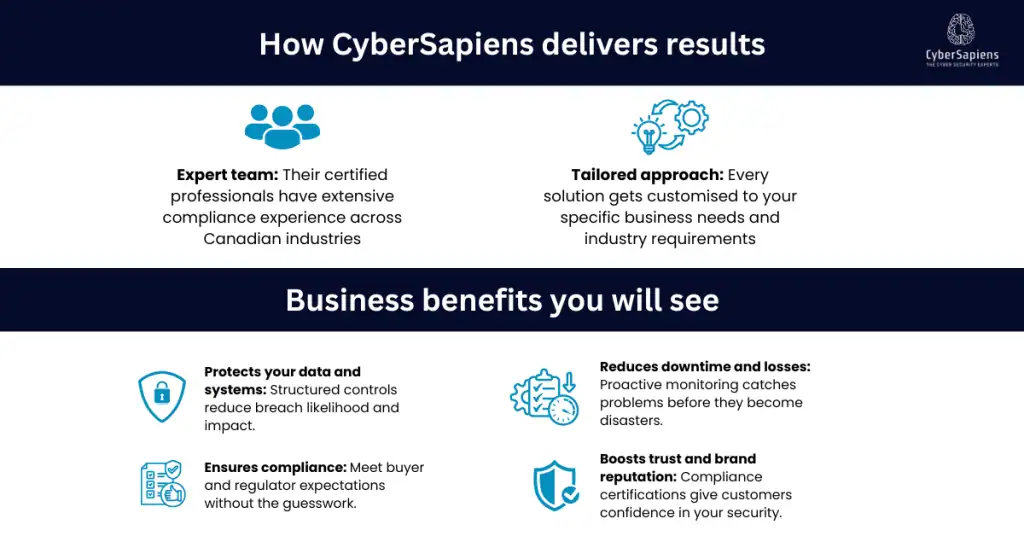
Expert team: Certified professionals with compliance experience across Canadian industries.
Tailored approach: Every solution customised to your business and industry requirements.
Reduces downtime: Proactive monitoring catches problems before they escalate.
Builds trust: Compliance certifications give customers confidence in your security posture.
2. PwC Canada
Overview: PwC Canada brings significant scale with thousands of professionals nationwide, with particular strength in Toronto and solid teams in Vancouver and Montreal. Best for large enterprises wanting a globally recognised audit brand.
3. Deloitte Canada
Overview: Deloitte Canada has extensive experience conducting SOC audits and can issue both Type 1 and Type 2 reports. Best for enterprises already working with Deloitte on other engagements.
4. KPMG Canada
Overview: KPMG Canada operates nationally with deep risk management expertise and the resources to handle complex, multi-framework engagements. Best for organisations needing SOC 2 bundled with wider risk advisory.
What these services include
Getting you ready for success
A thorough assessment maps out your systems, identifies data flows, and determines the controls you need.
Building the right foundation
Professional providers develop policies, procedures, and technical controls that fit your business, covering access management through incident response.
Making audits painless
Good compliance audit firms coordinate directly with certified auditors, so your documentation and evidence are ready without last-minute scrambling.
Keeping you compliant long-term
Managed compliance services include ongoing monitoring, regular testing, and evidence automation, since compliance is an ongoing relationship, not a one-and-done project.
Picking the right partner
1. Industry know-how matters
Healthcare companies need providers who understand HIPAA and provincial health acts. SaaS companies need cloud security expertise. Avoid generic solutions.
2. Clear timelines and realistic expectations
Reputable providers give structured project plans with real milestones. Typical timelines run four to eight months for Type 1 and eight to twelve months for Type 2.
3. Technology that actually helps
Modern providers use automated tools for evidence collection and monitoring, cutting manual work and giving real-time visibility into your compliance status.
Do not make these mistakes
Treating compliance like a one-time project. It is an ongoing commitment that requires continuous attention.
Writing policies nobody follows. Controls need to work in the real world, not just look good on paper.
Conclusion
Choosing the right SOC 2 and HIPAA compliance service provider in Canada is about protecting your business and opening new markets, not just ticking boxes. CyberSapiens stands out for its tailored strategies, ISO 27001 certification, and track record with Canadian businesses, whether you are a Toronto startup eyeing enterprise clients or a Vancouver health-tech company targeting U.S. markets.
CONTENT REVIEWED BY
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
FAQs
What is the difference between SOC 2 and HIPAA?
SOC 2 covers general security practices across industries. HIPAA specifically protects healthcare data for U.S. markets.
Do I need HIPAA if I only serve Canadian patients?
Usually not, unless you are handling U.S. healthcare data.
How long does SOC 2 take?
Type 2 typically takes eight to twelve months, including the evidence collection period.
Can I automate compliance?
Yes, modern platforms automate evidence collection and monitoring, though a human review is still part of a credible audit.
What is the most common audit finding?
Incomplete access reviews and inadequate documentation are the most frequently cited gaps.
Is Type 1 enough for enterprise sales?
Most enterprise buyers prefer Type 2 for sustained proof that controls actually operate over time, not just that they exist.
