
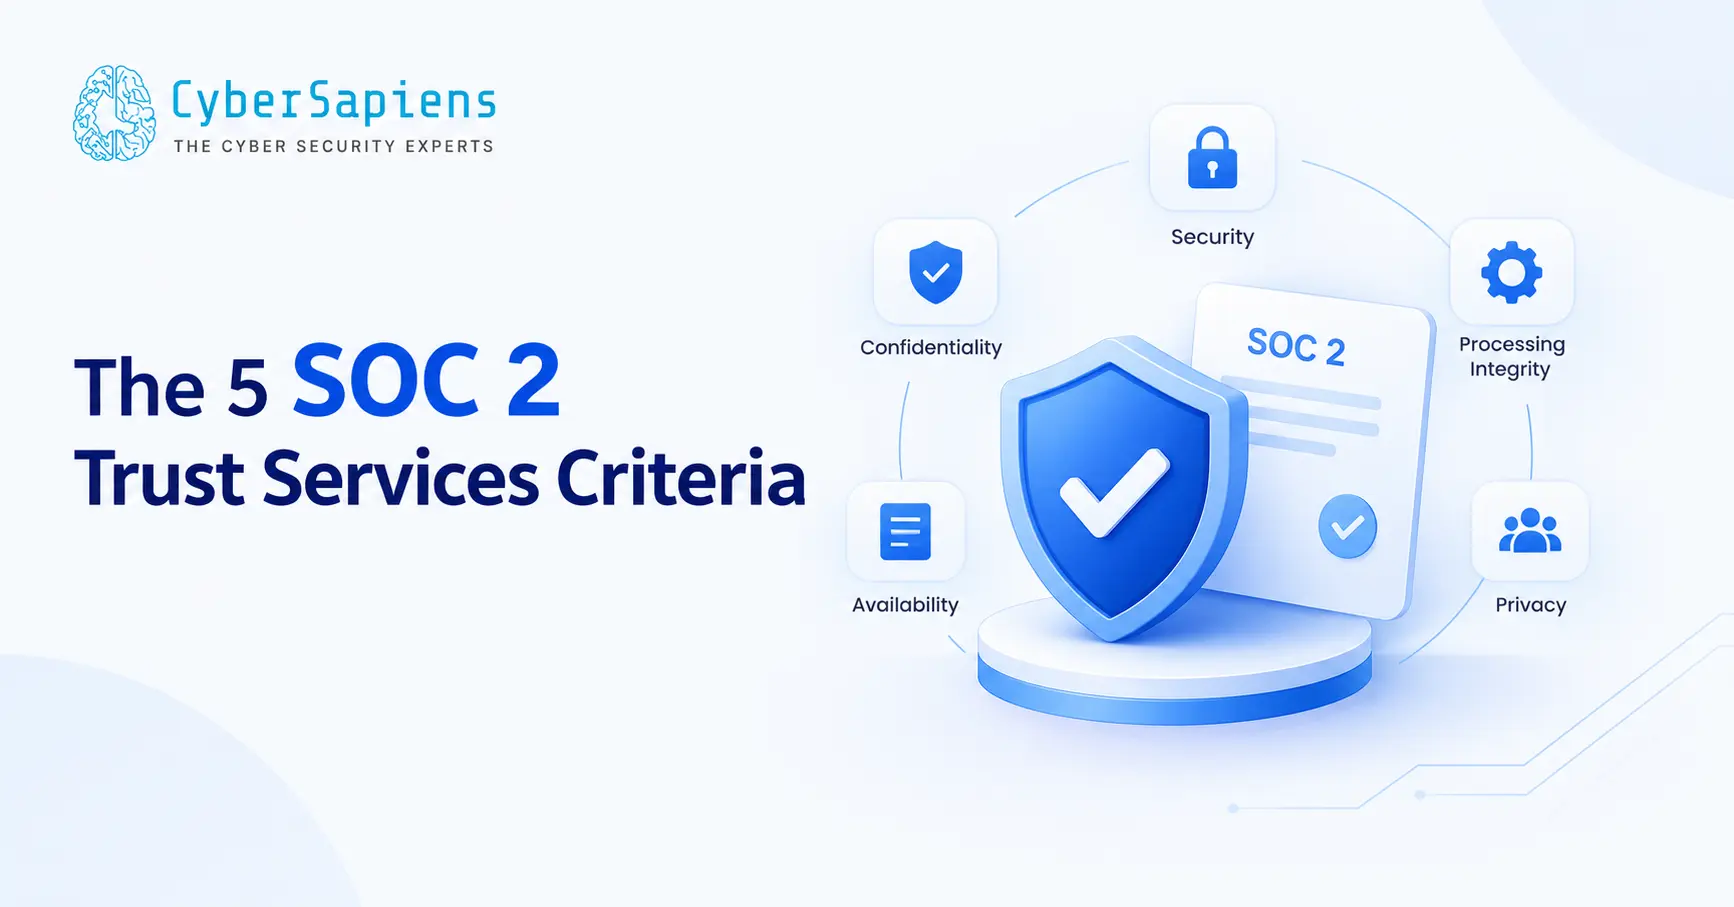
The 5 SOC 2 Trust Services Criteria Explained in Plain English
Quick Answer
SOC 2 has five trust services criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Security is the only mandatory one. The other four are added only when a specific customer, contract, or regulatory requirement calls for them.
The SOC 2 trust services criteria are the five categories an auditor can test during a SOC 2 report: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Every SOC 2 report must include Security. The other four are optional and are only added when a customer contract, regulator, or your own data handling model requires them.
In our work auditing Australian SaaS and cloud businesses, most companies start out assuming they need all five criteria because vendor security questionnaires list them together. In practice, the majority of first-time SOC 2 reports we scope only include Security, with additional criteria added later once a specific customer or regulatory requirement makes it necessary. The rest of this guide breaks down what each criterion actually covers, who needs it, and how the choice affects your cost and timeline.
The official definitions come from the AICPA Trust Services Criteria framework, which every SOC 2 audit is measured against.
The 5 Criteria at a Glance
Security
Protects systems against unauthorised access. Mandatory in every SOC 2 report.
Availability
Confirms your systems meet agreed uptime and performance commitments.
Processing Integrity
Confirms data processing is complete, accurate, timely, and authorised.
Confidentiality
Protects information designated as confidential, such as contracts or business data.
Privacy
Governs how personal information is collected, used, retained, and disclosed.
SOC 2 Trust Services Criteria Comparison Table
Use this table to see what each criterion actually tests, who typically needs it, and the type of evidence an auditor will ask for. In our audit engagements, the Confidentiality column comes up more often than people expect, particularly for professional services and B2B software firms handling client contracts and business data, while the Privacy criterion is usually reserved for organisations processing consumer personal information directly, such as healthcare or HR platforms.
| Criterion | What It Covers | Who Typically Needs It | Example Evidence |
|---|---|---|---|
| Security | Protection against unauthorised access, breaches, and system abuse. | Every SOC 2 report. This criterion is mandatory. | Access control logs, MFA enforcement records, firewall configurations. |
| Availability | System uptime, performance monitoring, and disaster recovery readiness. | SaaS platforms and infrastructure providers with uptime commitments in customer contracts. | SLA agreements, incident response logs, backup and failover test records. |
| Processing Integrity | Completeness, accuracy, timeliness, and authorisation of data processing. | Payment processors, e-commerce platforms, and businesses running data pipelines. | Transaction logs, quality control checks, error handling documentation. |
| Confidentiality | Protection of confidential business information, not necessarily personal data. | Firms handling client contracts, trade secrets, or intellectual property under NDA. | Non-disclosure agreements, encryption records, access restriction policies. |
| Privacy | Collection, use, retention, and disclosure of personal information. | Organisations processing consumer personal information directly, such as healthcare or HR platforms. | Privacy policies, consent records, data retention schedules. |
Why Most Companies Start With Security Only
Security is the only mandatory criterion in a SOC 2 report. Every other criterion is optional, and adding one that your customers do not actually require adds audit time, evidence collection, and cost without adding commercial value. This is the honest starting point most vendors and consultants skip, because a report that covers all five criteria looks more thorough, even when it is not what the customer asked for.
Across the SOC 2 engagements we scope for Australian SaaS and cloud businesses, the deciding factor is almost always the customer security questionnaire or contract clause that triggered the request. When we review that document with a client, it becomes clear which criteria are actually being asked for. In most first-time cases, that is Security alone.
Signs You Need More Than Security
Add Availability if
Your contract includes an uptime or SLA commitment your customer wants independently verified.
Add Processing Integrity if
Your platform processes transactions, payments, or data pipelines where accuracy is a customer concern.
Add Confidentiality if
You hold client contracts, trade secrets, or business data under a non-disclosure agreement.
Add Privacy if
You collect or process consumer personal information directly, such as in healthcare or HR platforms.
Not sure which criteria your customers actually require? Our team reviews your security questionnaires and contracts to confirm the right scope before your audit begins. Scope your criteria with CyberSapiens before committing to a full five-criteria audit.
How Your Criteria Choice Affects Cost and Timeline
Each additional trust services criterion beyond Security adds its own set of controls, evidence requests, and auditor testing hours. In the engagements we run for Australian businesses, the jump from a Security-only report to a two or three criteria report typically adds four to eight weeks to the readiness phase, mainly because of the extra evidence collection and control documentation involved rather than the audit itself.
| Scope | Typical Readiness Time | Relative Cost Impact | Main Cost Driver |
|---|---|---|---|
| Security only | Baseline timeline for a first-time report. | Lowest of the available options. | Access control and monitoring evidence only. |
| Security plus one criterion | Adds roughly four to eight weeks to readiness. | Moderate increase over baseline. | Additional control implementation and evidence for the added criterion. |
| Security plus two or more criteria | Longest readiness phase, especially for a first report. | Highest of the available options. | Overlapping but distinct evidence sets across multiple criteria. |
Customer security questionnaires are one of the most common triggers for scoping decisions, and standardised assessment frameworks such as the Cloud Security Alliance STAR programme can help you cross-reference what your customers are actually asking for before you commit to additional criteria. If you want a clear breakdown of Type 1 versus Type 2 costs on top of criteria selection, our SOC 2 costs and timelines guide covers this in detail.
Frequently Asked Questions
What are the SOC 2 trust services criteria?
The SOC 2 trust services criteria are the five categories a SOC 2 report can be assessed against: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Security is mandatory in every report, while the other four are added only when they are relevant to your business and your customers.
Do I need all 5 SOC 2 trust services criteria?
No. Most first-time SOC 2 reports include Security only, since this is the sole mandatory criterion. The remaining four are optional and should only be added when a customer contract, regulatory requirement, or your data handling model specifically calls for them.
Which SOC 2 criterion is mandatory?
Security is the only mandatory criterion in a SOC 2 report. It covers protection against unauthorised access and is included in every SOC 2 Type 1 or Type 2 report regardless of scope.
How do I choose which SOC 2 criteria to include?
Start by reviewing the customer security questionnaires or contract clauses that triggered your need for SOC 2. These documents usually specify exactly which criteria your customers expect, which prevents you from paying for scope you do not need.
Does adding more SOC 2 criteria increase the cost?
Yes. Each additional criterion adds its own controls and evidence requirements, which increases both readiness time and audit cost. This applies to both SOC 2 Type 1 and Type 2 reports, though the increase is larger for Type 2 given its longer observation period. See our SOC 2 Type 1 vs Type 2 guide for a full cost comparison.
Content Reviewed By
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
Not Sure Which SOC 2 Criteria You Actually Need?
CyberSapiens reviews your customer security questionnaires and contracts to confirm the right scope before your audit begins, so you are not paying for criteria your customers never asked for.
Get Certified