Top 10 SOC 2 Certification Consultants in Singapore
Quick answer: CyberSapiens is a leading SOC 2 certification consultant for Singapore-based businesses, offering end-to-end readiness, control implementation, and audit coordination. Other established providers include Privasec, Sekuro, and ISO Consultants Pte Ltd, each varying in scope, local presence, and pricing.
What is SOC 2 certification
SOC 2 is an audit framework developed by the American Institute of Certified Public Accountants (AICPA) that assesses an organisation’s controls across five Trust Services Criteria. Each report is tailored to the organisation being assessed, so no two SOC 2 reports look exactly alike.
Security
Availability
Processing Integrity
Confidentiality
Privacy
Why SOC 2 certification is important for businesses in Singapore
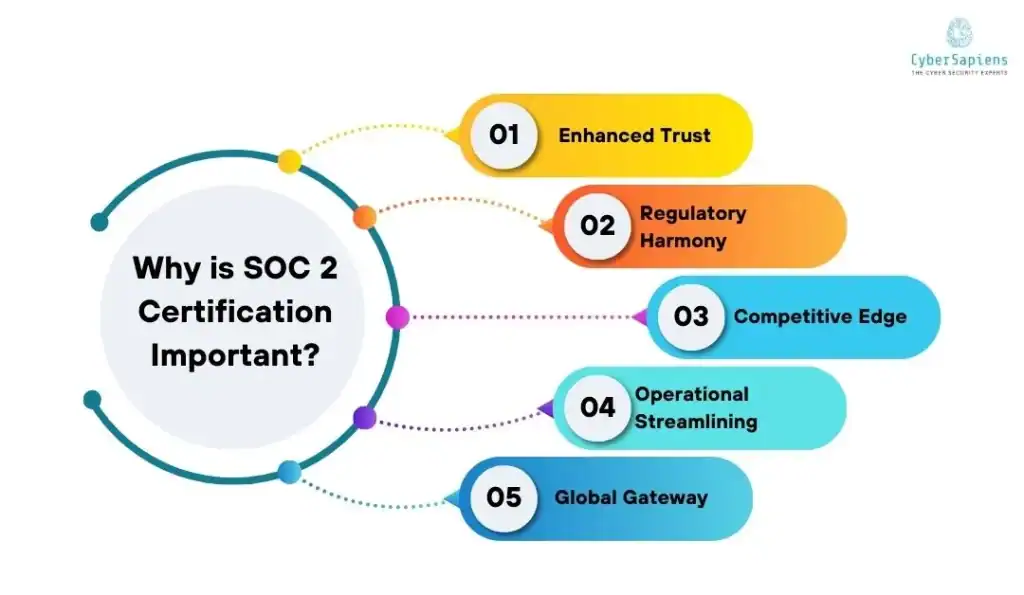
Enhanced trust
Demonstrates a verified commitment to data protection, differentiating your organisation in enterprise sales conversations where security assurance is non-negotiable.
Regulatory harmony
SOC 2 controls overlap significantly with Singapore’s Personal Data Protection Act (PDPA), which the Personal Data Protection Commission enforces, making SOC 2 readiness work double as groundwork for local compliance.
Competitive edge
Differentiates your organisation from competitors and strengthens your position when bidding for enterprise contracts in a crowded market.
Operational streamlining
The audit process surfaces inefficiencies and weak controls, giving you the chance to refine processes and reduce risk before they cause problems.
Global gateway
International clients, especially in the US, Europe, and Australia, often require SOC 2 as a precondition, making certification a direct route to cross-border partnerships.
Criteria for selecting a SOC 2 certification consultant
Proven track record: Years of experience and a portfolio of satisfied clients.
Local knowledge: Familiarity with Singapore’s regulatory environment, including PDPA.
Full-service offering: From pre-assessment through post-certification support.
Client testimonials: Real references or published case studies you can verify.
List of Top 10 SOC 2 Certification Consultants in Singapore
Below are the leading SOC 2 certification consultants serving Singapore businesses, evaluated on verified track record, service depth, and whether each has a genuine Singapore presence or serves the market remotely.
1. CyberSapiens
RECOMMENDEDBest SOC 2 Certification Consultant for Singapore Businesses
CyberSapiens is an ISO 27001:2022 certified cybersecurity and compliance firm helping Singapore businesses achieve SOC 2 certification end to end, from readiness assessment and gap analysis through control implementation, audit coordination, and employee security training.
What’s Included:
Scope definition and Trust Services Criteria mapping
Gap assessment and risk-prioritised remediation
Control implementation and policy development
Internal readiness audit before the official SOC 2 audit
Coordination with the external CPA firm through to certification
Employee security awareness training via the PhishCare platform
A Bengaluru-headquartered multi-standard certification consultancy offering SOC 2, ISO, and VAPT support with a no-fee-if-not-certified policy. Best for budget-conscious businesses comfortable with remote delivery. Serves Singapore remotely, no local office.
Founded in 2015 and headquartered in Bengaluru, Certvalue offers SOC 2, ISO, and other multi-standard certification consulting across many countries. Best for SMEs wanting a straightforward, affordable path to certification. Serves Singapore remotely, no local office.
Horangi
Singapore-headquartered cybersecurity firm founded by former Palantir engineers, among the first in Asia to achieve its own SOC 2 Type II certification. CREST-accredited, with the Gartner-recognised Warden cloud security platform. Best for cloud-native companies wanting a consultant that holds the same certification it helps clients achieve.
The largest pure-play cybersecurity service provider in Asia, headquartered in Singapore with offices across Malaysia, Hong Kong, and South Korea. Offers advisory and assurance services alongside managed security operations. Best for large enterprises wanting SOC 2 support bundled with broader security operations.
CertPro
A licensed CPA firm that issues SOC 2 attestation reports directly, with named Singapore clients including Giift and Perx Technologies. Best for organisations wanting readiness support and the final audit from a single provider. Serves Singapore clients directly as the issuing auditor.
Privasec
Founded in Australia in 2014, Privasec registered in Singapore and opened a local office in 2018, now operating as part of Sekuro. Offers GRC, offensive security, and digital transformation services. Best for organisations wanting a consultant with a genuine Singapore office and Australian-grade offensive security expertise.
B2BCert
A Bengaluru-headquartered certification consultancy offering SOC 1 and SOC 2 services across multiple countries, with documentation templates and audit readiness support. Best for cost-conscious businesses wanting structured paperwork support. Serves Singapore remotely, no local office.
A-LIGN
A certified CPA firm and the world’s top issuer of SOC 2 reports, with over 17,500 SOC assessments completed and a global audit team covering the Asia-Pacific region. Best for organisations juggling multiple frameworks who want one firm handling SOC 2, ISO 27001, and related audits together. Serves Singapore through its global delivery team, no dedicated local office confirmed.
Sekuro
An Australian-origin cybersecurity group and parent company of Privasec, offering strategic advisory and long-term risk management across the Asia-Pacific region. Best for organisations wanting strategic, long-horizon security planning alongside SOC 2 certification work.
Criteria for Selecting a SOC 2 Certification Consultant
With several consultants serving the Singapore market, the right choice depends on more than price. Here is what actually matters when comparing providers.
Proven Track Record
Years of SOC 2 engagements and client outcomes you can actually verify, not just a client logo wall.
Local Market Knowledge
Familiarity with Singapore’s PDPA and how it interacts with SOC 2’s Trust Services Criteria, rather than a generic global playbook.
Full-Service Offering
Coverage from pre-assessment through post-certification support, so no stage is handed off to a different vendor midway.
Verifiable Client References
Named clients or case studies you can check independently, not unattributed testimonials.
Transparent Scope and Pricing
A clearly defined engagement scope agreed before work begins, with no ambiguity about what’s included.
Benefits of Engaging a SOC 2 Consultant
Expertise on Tap
Access to specialists who have run SOC 2 engagements repeatedly, rather than learning the framework for the first time internally.
Faster Certification
A structured, proven process cuts months off a self-guided timeline, particularly for a first SOC 2 audit.
Reduced Audit Risk
An experienced consultant catches control gaps before the official audit, lowering the chance of a failed or delayed attestation.
Continuous Improvement
Ongoing audits and control reviews keep the security programme current as systems, vendors, and threats evolve.
Conclusion
SOC 2 certification has become a baseline expectation for Singapore businesses handling customer data, particularly those serving international clients in the US, Europe, and Australia who routinely require it as part of vendor due diligence. Choosing the right consultant shapes how smoothly that journey goes.
Whether you are a startup pursuing your first SOC 2 report or an established enterprise maintaining ongoing compliance, prioritise a consultant with a verifiable track record, genuine familiarity with Singapore’s regulatory environment, and transparent scope and pricing. CyberSapiens offers exactly that combination for Singapore businesses navigating their SOC 2 journey.
Book Your Free SOC 2 ConsultationFAQs: SOC 2 Certification Consultants in Singapore
Common questions from Singapore businesses evaluating SOC 2 certification.
What’s the difference between SOC 2 Type I and Type II?
A Type I report assesses whether your controls are designed appropriately at a single point in time, while a Type II report evaluates whether those controls actually operated effectively over a period, typically six to twelve months. Most enterprise buyers, including those in Singapore, treat Type II as the standard expectation rather than Type I alone.
How long does SOC 2 certification take in Singapore?
Most organisations complete SOC 2 certification in 3 to 6 months, covering gap assessment, remediation, the control observation period, and the final audit. A Type II report specifically requires a multi-month observation window, so the timeline rarely compresses much below that regardless of how prepared you are going in.
What’s the ballpark cost for SOC 2 in Singapore?
Auditor fees for a SOC 2 Type II report in Singapore typically run SGD 15,000 to 100,000 or more, with total first-year cost, including readiness assessment, consultant support, and remediation, often landing between SGD 25,000 and 150,000 depending on company size and scope. Smaller, well-prepared organisations sit toward the lower end of that range.
Can small businesses afford SOC 2?
Yes, several consultants specialise in budget-conscious engagements for smaller organisations, and starting with a Type I report before progressing to Type II is one way to spread the cost and timeline. Many small businesses pursue certification specifically because an enterprise client or investor requires it, which makes the cost a market-access decision rather than a discretionary one.
Does SOC 2 cover GDPR?
No, SOC 2 and GDPR overlap on data privacy principles but are separate frameworks with different legal bases and requirements. SOC 2’s privacy criteria can support GDPR readiness, but achieving SOC 2 does not by itself satisfy GDPR obligations, and organisations handling EU personal data still need a dedicated GDPR compliance review.
Ready to Achieve SOC 2 Certification?
CyberSapiens guides Singapore businesses through the full SOC 2 journey, from readiness assessment to final certification. Book a free consultation to get started.
