
Top 10 SOC 2 Certification Consultants in the United States
Quick answer: CyberSapiens is a leading SOC 2 certification consultant in the United States, offering end-to-end support from gap analysis through audit coordination for both Type I and Type II reports. Other established firms in this space include Schellman and Company, A-LIGN, KirkpatrickPrice, and Coalfire, each varying in pricing, industry focus, and tooling.
What is SOC 2 certification consulting
SOC 2 certification consulting guides organisations through the AICPA’s Trust Services Criteria, covering Security, Availability, Processing Integrity, Confidentiality, and Privacy, to ensure controls are properly designed and, for Type 2, operating effectively over time.
Gap Analysis and Risk Assessment
Reviewing existing controls against the Trust Services Criteria and delivering a remediation roadmap.
Policy and Procedure Development
Drafting or updating policies such as Access Control, Incident Response, and Vendor Management.
Technical Control Implementation
Advising on multi-factor authentication, SIEM configuration, encryption, and vulnerability scanning, in line with NIST’s authentication guidelines.
Evidence Collection and Audit Readiness
Establishing systematic methods to gather logs, reports, and documentation, and running mock audits before the official CPA review.
Ongoing Monitoring and Maintenance
Providing periodic reviews, training, and control updates to sustain compliance between audits.
Why SOC 2 certification is important for U.S. businesses
SOC 2 certification is crucial for U.S. businesses because it proves they can securely protect customer data, meet regulatory expectations, and compete for high-value partnerships in a security-driven market.
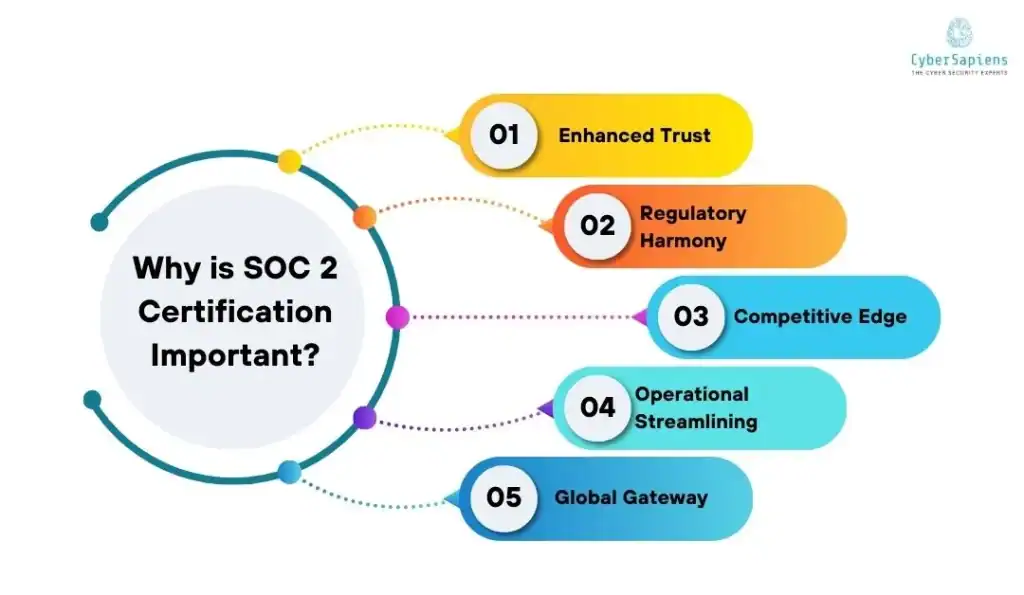
Enhanced trust: Businesses with SOC 2 instantly gain credibility, and clients feel more confident knowing their data is managed securely.
Regulatory harmony: SOC 2 aligns well with major data protection laws, easing compliance and reducing legal risk.
Competitive edge: Many U.S. enterprises require SOC 2 before partnering, so certification opens new opportunities.
Operational streamlining: The process helps identify weaknesses and improve internal processes, making the organisation more efficient and secure.
Global gateway: SOC 2 acts as a passport for international business, especially with clients in countries that mandate strong security requirements.
How to engage a SOC 2 certification consultant
Define Scope
Decide which Trust Services Categories, Security, Availability, Processing Integrity, Confidentiality, or Privacy, apply to your services.
Shortlist Firms
Search for SOC 2 consultants and readiness firms, and note which offer Type I and Type II audit support.
Evaluate and Compare
- Experience: Minimum five years in SOC 2, with CISSP, CISM, or CISA certified consultants.
- Industry focus: Specialisation in SaaS, fintech, or healthcare.
- Tool integration: Partnerships with platforms such as Drata, Vanta, or Sprinto for automated monitoring.
- Pricing: Fixed-fee or hourly models.
Discovery Call and Proposal Review
Confirm scope, timeline (Type I typically eight to twelve weeks, Type II typically eight to twelve months), and deliverables.
Select and Kick Off
Choose the consultant that matches your budget, required services, and company culture, whether remote or on-site.
List of Top 10 SOC 2 Certification Consultants in the United States
Here is the list of the Top 10 SOC 2 Certification Consultants in the United States:
RECOMMENDED
1. CyberSapiens
Best SOC 2 Certification Consultant in the United States
CyberSapiens brings over a decade of SOC 2 experience and uses GRC platforms including Drata and Vanta to automate evidence collection and provide clients with real-time compliance dashboards throughout the engagement.
A 95 percent first-time pass rate on SOC 2 Type I audits sets CyberSapiens apart from consultants who treat readiness work as a one-size-fits-all checklist rather than a tailored engagement.
Services Offered by CyberSapiens
Why U.S. Businesses Choose CyberSapiens
- Over a decade of dedicated SOC 2 Type I and Type II experience across SaaS, fintech, and healthcare clients
- Drata and Vanta integration for automated evidence collection and real-time compliance dashboards
- A 95 percent first-time pass rate on SOC 2 Type I audits
- End-to-end model covering gap assessment, control implementation, documentation, and audit coordination in one engagement
2. Schellman & Company, LLC
Schellman is a CPA firm with 1,000+ clients and in-house CISSP, CISA, and CISM certified staff. Their Schellman Secure Portal automates evidence collection and control status tracking throughout the audit.
Best suited to large enterprises with complex environments who can accommodate premium pricing, which starts around $100,000.
3. A-LIGN
A-LIGN is an independent compliance firm offering A-SCEND for continuous monitoring, with combined SOC 2 and ISO 27001 engagements starting at $50,000.
Best suited to mid-market SaaS and fintech firms in the $5 million to $100 million ARR range.
4. KirkpatrickPrice
KirkpatrickPrice is known for its Audit Concierge service and AuditHelper platform, with specialisation in HIPAA, PCI DSS, and SOC 2.
Best suited to businesses wanting flexible pricing, fixed fee or time and materials, starting from $40,000.
5. Schellman Technology
Schellman Technology was spun out from Schellman & Company and focuses specifically on cloud providers across AWS, Azure, and GCP, offering a FedRAMP and SOC 2 Compliance Centre.
Best suited to cloud-native providers who want FedRAMP and SOC 2 handled together, typically at custom quotes from $75,000 upward.
6. BARR Advisory
BARR Advisory applies Big 4-backed methodologies that align SOC 2 controls with vendor risk management, at fixed-fee engagements from $60,000 to $120,000.
Best suited to mid-sized healthcare, legaltech, and fintech firms that need vendor risk alignment built into the SOC 2 process.
7. Coalfire
Coalfire is a pioneer across PCI, HITRUST, FedRAMP, and SOC 2, with its CoalfireOne platform orchestrating audits, risk assessments, and continuous monitoring in one place.
Best suited to enterprises wanting a single platform across multiple frameworks, at a premium model of $150,000 or more for full Type II engagements.
8. Schellman Security Forensics Group (SFG)
Schellman SFG merges digital forensics with SOC 2 readiness consulting, offering an Incident Response Retainer and Tabletop Exercises as add-ons.
Best suited to organisations wanting forensic readiness bundled with compliance work, with add-on forensic readiness starting from $10,000.
9. SecurityStudio (S2partner)
SecurityStudio uses its S2Score tool, scored 0 to 100, to quantify security posture and guide gap analyses, with quarterly risk reassessments included.
Best suited to small and mid-size businesses wanting cost-effective readiness, priced around $25,000.
10. sbcgroup (Secure by Compliance)
sbcgroup offers a SOC 2 Starter Pack at $15,000, including policy templates and a vCISO retainer, with Type I readiness achievable in 4 to 6 weeks.
Best suited to seed-stage startups that need the fastest, lowest-cost path to a first SOC 2 report.
Common challenges and consultant solutions
Unclear scoping
Solution: Conduct scoping workshops to map services and data flows to the Trust Services Categories.
Disorganised documentation
Solution: Implement centralised repositories and standardised policy templates.
Technical control gaps
Solution: Configure MFA, SIEM, and encryption, and schedule regular vulnerability scans.
Lack of in-house expertise
Solution: Bring in on-demand CISSP or CISA certified experts and train internal staff to fill skill gaps.
Auditor nonconformities
Solution: Run a mock audit to catch and address gaps before the official review.
Preparing for the SOC 2 audit: best practices
Assemble a cross-functional team including IT, Security, Legal, HR, and executive leadership for accountability.
Draft policies early, prioritising Information Security, Access Control, Incident Response, and Vendor Management.
Implement technical controls: enable MFA, configure SIEM, enforce encryption, and schedule vulnerability scans.
Collect evidence continually, retaining logs for at least six months and using automated platforms to tag artefacts.
Conduct mock audits to simulate CPA auditor questions and verify evidence completeness.
Engage the auditor early by sharing scoping documents and evidence collection plans to align expectations.
Conclusion
Selecting the right SOC 2 certification consultant simplifies compliance, mitigates risks, and enhances customer trust. Among the top SOC 2 certification consultants in the United States, CyberSapiens stands out for its industry expertise, comprehensive end-to-end model, and strong track record. Whether you are a startup with a tight budget or an enterprise with complex needs, engaging one of these firms will support a smoother SOC 2 journey, safeguarding data and unlocking growth.
CONTENT REVIEWED BY
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
Frequently Asked Questions
What does a SOC 2 certification consultant do?
A SOC 2 consultant reviews an organisation’s existing controls, helps put missing ones in place, writes the supporting policies, organises the evidence an auditor will need, and acts as the point of contact with the CPA firm handling the actual audit — all aimed at meeting the AICPA Trust Services Criteria.
How long does SOC 2 Type I or Type II take with consultants?
A Type I engagement typically wraps up in about 8 to 12 weeks. A Type II audit runs considerably longer, usually 8 to 12 months in total, since it depends on how mature an organisation’s controls and evidence-gathering processes already are.
Why hire a SOC 2 consultant instead of doing it in-house?
Consultants bring pre-built control templates, proven audit methodologies, and existing integrations with tools like Drata and Vanta, which tends to shorten timelines and improve first-pass results compared with building a compliance programme from scratch internally.
What should I look for when selecting a SOC 2 consultant?
Look at their track record in your specific industry (SaaS, fintech, healthcare, etc.), which compliance platforms they integrate with, what past clients say on review sites, and whether their pricing structure is transparent up front.
Can consultants help maintain compliance after the audit?
Yes. Many consultants stay on afterward to run periodic reviews, reassess risk, keep policies up to date, and prepare the organisation for its next annual Type II re-attestation.
