
Why CyberSapiens is the Right Partner for SOC 2 Type 2 Compliance in India
Quick answer: CyberSapiens is a strong SOC 2 Type 2 partner for Indian companies because it offers end-to-end support, from gap analysis and control implementation through to audit coordination and certification, backed by hands-on consultants with India and global compliance experience across SaaS, IT, and healthcare. This full-cycle support typically shortens the six-to-twelve-month certification timeline and strengthens client trust with international buyers.
Every global client today asks one common question: “Are you SOC 2 Type 2 compliant?”
For Indian companies in SaaS, IT services, FinTech, healthcare, and outsourcing, this is not just a compliance checkbox. It is a foundation of trust. Without it, scaling into global markets becomes harder, and customer confidence weakens.
At CyberSapiens, we help Indian businesses prepare, audit, and achieve SOC 2 Type 2 certification. This ensures they meet international security and compliance expectations.
What is a SOC 2 Type 2 Report?
A SOC 2 Type 2 report assesses a company’s ability to manage security, availability, processing integrity, confidentiality, and privacy over a specified period, typically ranging from six to twelve months.
Unlike a one-time check, this report validates that your controls are not just designed but are working effectively in real operations. Global clients rely on it before trusting you with their data.
Difference between SOC 2 Type 2 vs Type 1
| Factor | SOC 2 Type 1 | SOC 2 Type 2 |
|---|---|---|
| Focus | Design of controls | Design and operating effectiveness |
| Depth | Limited assurance | High assurance |
| Preferred by | Smaller clients, early-stage businesses | Global enterprises, regulated industries |
| Timeline | Single point in time | 6 to 12 months monitoring |
If you are targeting enterprise or international clients, SOC 2 Type 2 certification is the preferred choice.
SOC 2 compliance in India: why it is growing
Indian companies are expanding globally. With SaaS, healthcare outsourcing, IT services, and FinTech growing internationally, SOC 2 compliance in India, built on the AICPA’s Trust Services Criteria, has become a business necessity.
SaaS companies need it for US and EU clients.
Healthcare BPOs need it for HIPAA alignment.
FinTech startups need it for investor and client confidence.
Without SOC 2 Type 2, global deals can get delayed or lost.
Benefits of SOC 2 Type 2 certification
Decision-makers often ask if this effort is worth it. The benefits go beyond compliance.
Customer trust: Shows your company protects sensitive data.
Global market entry: Essential for signing overseas clients.
Competitive advantage: Stand out from non-compliant competitors.
Regulatory alignment: Helps with HIPAA, GDPR, and ISO 27001:2022.
Operational maturity: Improves internal processes and risk management.
Benefits of SOC 2 Type 2 certification
Decision-makers often ask if this effort is worth it. The benefits go beyond compliance.
Customer trust: Shows your company protects sensitive data.
Global market entry: Essential for signing overseas clients.
Competitive advantage: Stand out from non-compliant competitors.
Regulatory alignment: Helps with HIPAA, GDPR, and ISO 27001:2022.
Operational maturity: Improves internal processes and risk management.
Why choose CyberSapiens for SOC 2 Type 2 compliance in India
CyberSapiens acts as a complete compliance partner.
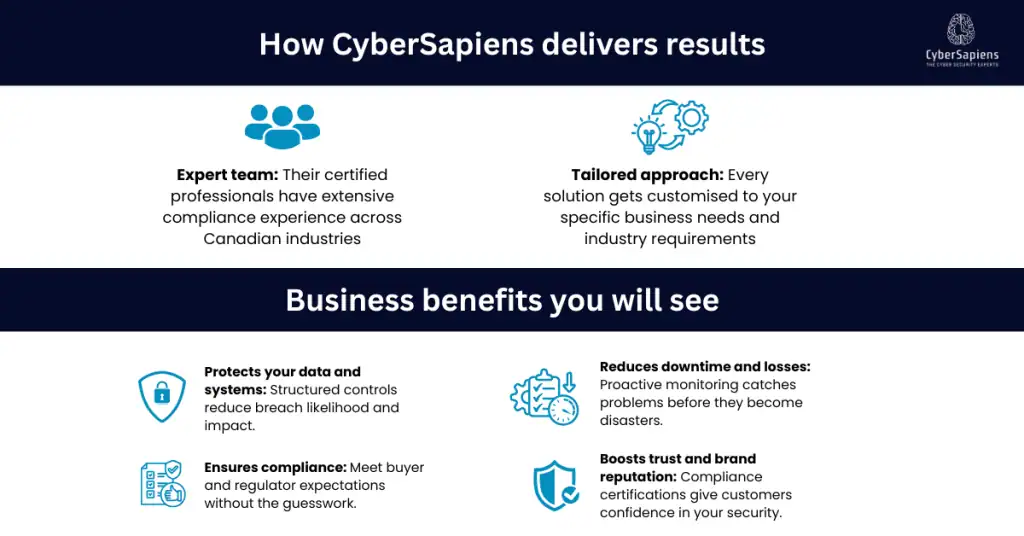
End-to-end support: From gap analysis to audit readiness.
India and global experience: Worked with SaaS, IT, and healthcare companies scaling abroad.
Hands-on experts: Consultants simplify compliance and make it actionable.
Practical roadmap: Tailored for your company size and industry.
Our approach ensures faster certification and stronger trust with clients.
Conclusion
Achieving SOC 2 Type 2 compliance is no longer optional for Indian companies aiming for global clients. It is a demonstration of trust, reliability, and operational maturity. From SaaS and FinTech to healthcare and IT services, organisations that invest in SOC 2 Type 2 certification gain a clear competitive advantage while ensuring their data management practices meet international standards.
Partnering with CyberSapiens ensures a smooth journey from preparation to audit, helping your company not only achieve certification but also strengthen client confidence and open doors to global opportunities.
Content Reviewed By
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
FAQs
1. What is SOC 2 Type 2 compliance?
Answer: It is a framework that ensures systems are secure, available, reliable, confidential, and private. An independent audit validates it over time.
2. How long does SOC 2 Type 2 certification take?
Answer: Answer: Usually six to twelve months, depending on company readiness and audit scope.
3. What is the difference between SOC 2 Type 1 and Type 2?
Answer: Soc 2 Type 1 checks the design of controls at a single point. Soc 2 Type 2 validates the design and performance over time.
4. Do Indian companies need a SOC 2 Type 2 audit?
Answer: Yes, if they want to work with US or EU clients or regulated industries, it is often required.
5. How much does SOC 2 compliance cost in India?
Answer: It varies with company size, systems, and scope. Startups may spend less, while enterprises require deeper audits.
