
Top 10 SOC 2 Type 2 Compliance Service Providers in the United Kingdom
Quick answer: CyberSapiens is a leading SOC 2 Type 2 compliance service provider for UK organisations, alongside major firms such as KPMG UK, PwC UK, and EY UK. SOC 2 Type 2 certification evaluates how effectively your security controls operate over a defined period, typically six to twelve months, giving UK businesses a credible way to demonstrate data protection commitments to customers and partners.
Introduction to SOC 2 Type 2 compliance
SOC 2 is divided into two types. Type 1 attests to the design of an organisation’s controls at a single point in time, while Type 2 is a more comprehensive examination that assesses the operating effectiveness of those controls over a specified period. Both are built on the AICPA’s Trust Services Criteria.
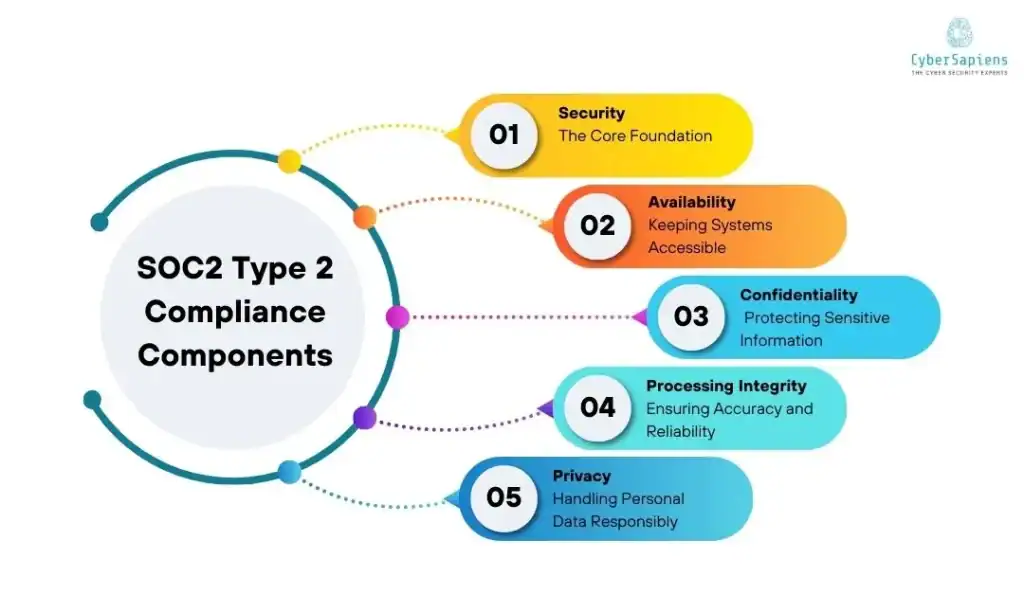
1. Security
The system is protected against unauthorised access, unauthorised processing, and unauthorised modifications to ensure the confidentiality, integrity, and availability of data.
2. Availability
The system is available for use and operation as agreed upon, ensuring that data is accessible when needed.
3. Confidentiality
Confidential data is protected as agreed upon between the organisation and its customers.
4. Processing integrity
System processing is complete, accurate, timely, and authorised.
5. Privacy
Personal information is collected, used, retained, and disposed of in accordance with the organisation’s privacy notice and applicable laws and regulations.
List of top 10 SOC 2 Type 2 compliance service providers in the United Kingdom
Typical UK SOC 2 Type 2 engagement fees range from roughly £12,000 to £55,000, depending on firm size, scope, and whether the audit is bundled with ISO 27001.
1. CyberSapiens: Best SOC 2 Type 2 Compliance Service Provider in the United Kingdom
CyberSapiens provides all types of SOC compliance, be it SOC 1 or SOC 2, following a structured framework and guidelines built to meet client requirements across multiple regulatory jurisdictions.
CyberSapiens SOC 2 Type 2 Compliance Process
1. Define Scope: Identifies which systems, services, and processes are part of the SOC 2 assessment.
2. Current State Analysis: Reviews existing security controls and operational practices.
3. Control Mapping: Matches existing controls against the SOC 2 Trust Services Criteria.
4. Gap Assessment: Identifies control deficiencies or missing elements.
5. Risk Analysis: Assesses security, availability, confidentiality, and other SOC 2-related risks.
6. Implementation: Puts required controls, procedures, and policies into action.
7. Internal Audit: Confirms implemented controls are functioning properly before the formal review.
8. External Audit: A qualified third-party auditor evaluates controls over the defined period for SOC 2 Type 2.
2. KPMG UK
Overview: A Big Four firm offering SOC 2 Type 2 reporting as part of its wider audit, tax, and advisory practice, issued through its US-licensed CPA affiliate. Best for large enterprises and regulated organisations already working with KPMG on other engagements.
3. PwC UK
Overview: PricewaterhouseCoopers offers SOC 2 Type 2 readiness assessments, gap analysis, and audit support, drawing on its global attestation network. Best for multinational organisations needing SOC 2 coordinated across several jurisdictions.
4. Ernst and Young (EY) UK
Overview: EY’s advisory practice includes SOC 2 Type 2 control design, implementation, and risk management support, delivered through its global professional network. Best for enterprises wanting SOC 2 integrated into a broader risk advisory relationship.
5. BDO UK
Overview: BDO UK is an independently confirmed SOC 2 report-issuing audit firm, part of the international BDO network. Best for growing and established mid-market businesses wanting a personalised approach without a Big Four price tag.
6. Mazars UK
Overview: Now operating as Forvis Mazars UK, this global audit, tax, and advisory firm provides SOC 2 Type 2 compliance services, confirmed as an active UK SOC 2 auditor. Best for organisations wanting a global network firm with a London base.
7. Grant Thornton UK
Overview: Confirmed as a top-tier UK CPA firm for SOC 1, 2, and 3 reports, operating as Grant Thornton UK Advisory and Tax LLP. Best for UK and international mid-market to enterprise clients needing assurance reports recognised by US and European counterparties.
8. RSM UK
Overview: RSM UK is a well established audit, tax, and consulting firm offering SOC 2 Type 2 compliance services alongside readiness assessment and gap remediation. Best for mid-sized UK businesses wanting a single advisory firm for both finance and compliance needs.
9. BSI Group
Overview: BSI Group is an internationally recognised assurance provider confirmed to serve UK FinTech and regulated financial services clients needing SOC 2 alongside DORA, ISAE 3402, or ISAE 3000 reports. Best for UK FinTech firms needing SOC 2 combined with European regulatory attestation.
10. CertPro
Overview: CertPro is a licensed CPA firm confirmed to conduct SOC 2 Type 1 and Type 2 audits for organisations operating across the UK, with a client base including SaaS and fintech companies. Best for startups and scale-ups pursuing their first SOC 2 report.
Choosing the right SOC 2 Type 2 compliance service provider
With numerous service providers available, choosing the right one can be daunting. Because a SOC 2 report must be issued by a licensed CPA firm, UK organisations should also confirm that any shortlisted provider has genuine attestation-issuing authority rather than offering readiness consulting alone.
1. Experience
Look for providers with extensive experience in SOC 2 compliance, particularly in your industry.
2. Expertise
Ensure the provider has a team with the necessary expertise to guide you through the compliance process from scoping through audit.
3. Customisation
Opt for a provider that offers tailored services to meet your organisation’s specific needs and challenges, rather than a one-size-fits-all package.
4. Reputation
Research the provider’s reputation and ask for references to gauge their reliability and effectiveness, including how they handle third-party and supply chain risk, an area the UK’s National Cyber Security Centre treats as central to vendor assurance.
5. Cost
Consider the cost of the services and ensure they align with your budget and expectations, keeping in mind that UK SOC 2 Type 2 engagements typically range from roughly £12,000 to £55,000 depending on scope.
Conclusion
SOC 2 Type 2 compliance takes real planning, but the right provider makes it far more manageable. Among the firms covered here, CyberSapiens stands out for its end-to-end approach, from scoping through external audit, backed by a track record across SOC 1 and SOC 2 engagements. Whichever provider you choose, prioritising genuine attestation experience over price alone will pay off in a smoother audit and a report your customers can actually rely on.
CONTENT REVIEWED BY
Ketki Tidke
Cyber Security and GRC Lead Auditor
ISO 27001 Lead Auditor
Ketki is a certified ISO 27001 Lead Auditor specialised in Governance, Risk and Compliance, with experience consulting public, private, and government clients. She evaluates threats, risk impacts, and regulatory requirements across multiple industry frameworks.
FAQs
Why is SOC 2 Type 2 compliance important?
SOC 2 Type 2 compliance is crucial for organisations that handle sensitive customer data, as it demonstrates their commitment to securing and protecting this information. It also helps build trust with customers and stakeholders, and is increasingly expected by US and enterprise buyers during vendor reviews.
What is the difference between SOC 2 Type 1 and SOC 2 Type 2?
SOC 2 Type 1 is an attestation of the design of an organisation’s controls at a single point in time, while SOC 2 Type 2 is a more comprehensive examination that assesses the operating effectiveness of those controls over a specified period, typically six to twelve months.
How long does it take to achieve SOC 2 Type 2 compliance?
The time it takes can vary depending on the complexity of the organisation, the extent of the controls, and existing readiness. On average, it takes several months to a year or more, since the Type 2 audit period itself typically runs six to twelve months before a report can be issued.
Do all organisations need to achieve SOC 2 Type 2 compliance?
Not all organisations need SOC 2 Type 2 compliance, but it is highly recommended for those that handle sensitive customer data, such as cloud service providers, software-as-a-service providers, and financial institutions. SOC 2 is not a legal requirement in the UK, but it is frequently expected by US customers and enterprise buyers during procurement.
How much does SOC 2 Type 2 compliance cost in the UK?
The cost can vary widely depending on the size and complexity of the organisation and the scope of controls being audited. UK SOC 2 Type 2 engagements typically range from roughly £12,000 to £55,000, with large enterprise or multi-framework engagements costing more.
How often does an organisation need to undergo a SOC 2 Type 2 audit?
A SOC 2 Type 2 audit is typically performed annually to maintain a current report, though the frequency may vary depending on the specific needs of the organisation and the requirements of its customers or stakeholders.
