Posted on October 25th, 2026 by Ketki Tidke
Quick answer: This guide covers eleven providers of cloud security testing, listed alphabetically and not ranked. We list firms whose own websites or official registers confirm a testing or related service, and we say where cloud testing is not named. For UK buyers, the checks that matter are CREST accreditation, the NCSC CHECK scheme for […]
Posted on October 25th, 2026 by Ketki Tidke
Quick answer: enum4linux is a command-line tool that asks Windows and Samba systems what they will reveal over SMB, such as users, shares, groups and the password policy. Use it only on systems you have written permission to test, and treat what it finds as evidence to report and fix, not a list to attack. […]
Posted on October 23rd, 2026 by Ketki Tidke
Quick answer: This guide covers seven penetration testing providers whose own websites we could check, listed alphabetically and not ranked. Only some state a Canadian office, so we show what each site says and leave out what we could not confirm. Pick by your rules (PIPEDA, OSFI Guideline B-13, customer contracts), tester credentials and proposal […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER Who are the best ISO 27001:2022 service providers in Canada? There is no single best provider, because ISO 27001 services come in two kinds: certification bodies that audit and certify you, and consultants that build your ISMS. Choose one of each and keep them separate, and check the certification body’s accreditation in the […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER What does the ISO 27001 move from 2013 to 2022 mean for your business now? The transition period ended on 31 October 2025, so ISO 27001:2013 certificates are no longer valid. If you transitioned in time, keep your ISMS aligned with the 2022 edition and its 2024 amendment. If you did not, you […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER What is the best ISO 27001:2022 service provider in the UAE? The best choice depends on the job, because the certificate and the preparation come from different types of provider. For the audit and certificate, choose a certification body accredited for ISO/IEC 27001 by the Emirates International Accreditation Centre (EIAC) or another IAF […]
Posted on October 6th, 2026 by Cyber
QUICK ANSWER When to hire a vCISO comes down to one question: is anyone senior accountable for cyber risk at the moment an outside pressure forces the issue? If the answer is no, and a regulator, customer, insurer or board member is asking, it is time to bring one in. The three loudest signs are: […]
Posted on August 4th, 2026 by Cyber
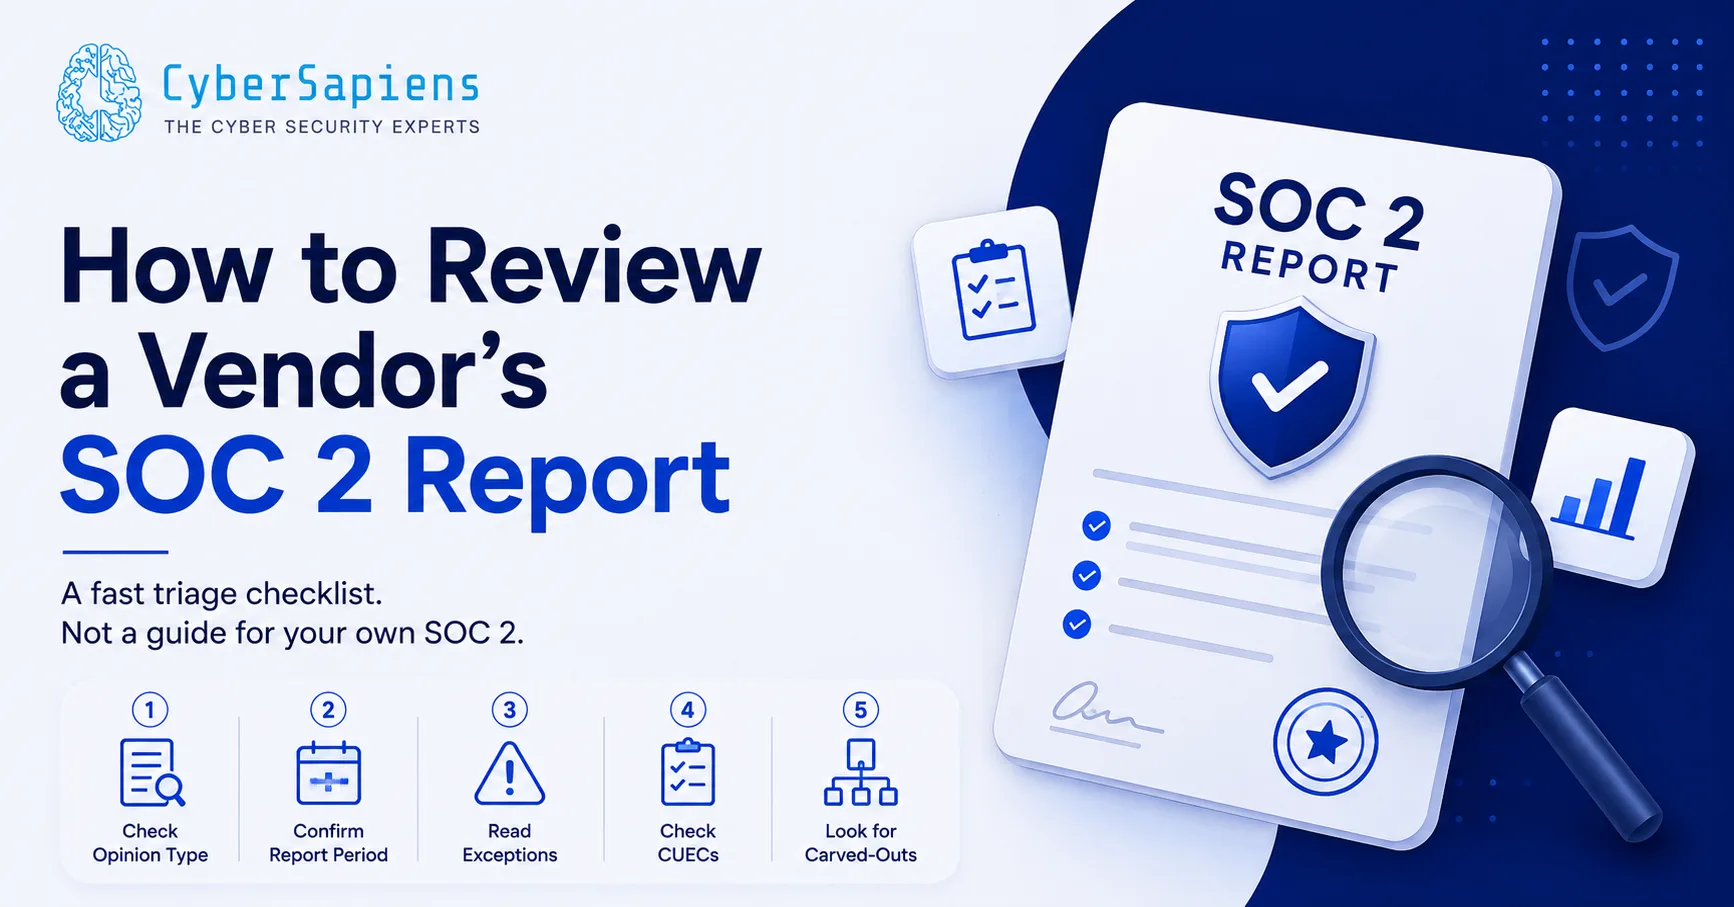
A SOC 2 report can run to 60 or more pages, and most of it is not what you actually need to check. Five things matter most: the auditor’s opinion type, the report period, any exceptions listed, the complementary user entity controls, and whether any subservice organisations are carved out of scope. Check those five […]
Posted on July 31st, 2026 by Cyber
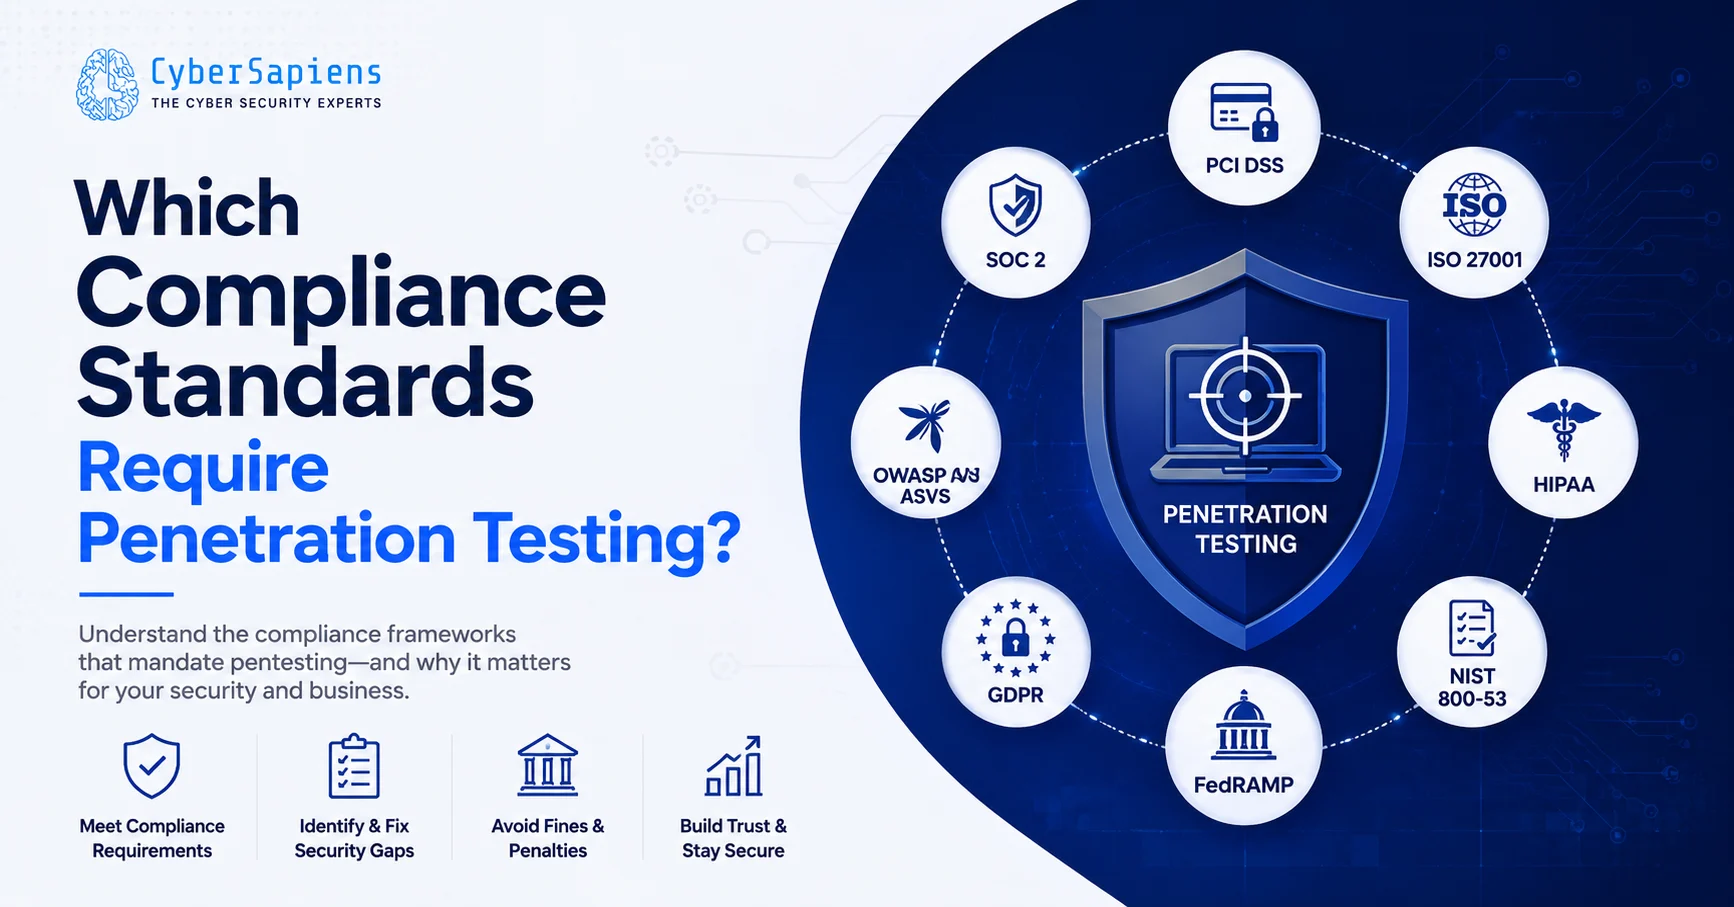
Not every compliance framework treats penetration testing the same way. Some name it explicitly and set a strict schedule. Others imply it through a broader control requirement and leave the frequency to your auditor’s judgement. Knowing which is which before you scope an engagement saves you from either under-testing and failing an audit, or over-testing […]
Posted on July 29th, 2026 by Cyber
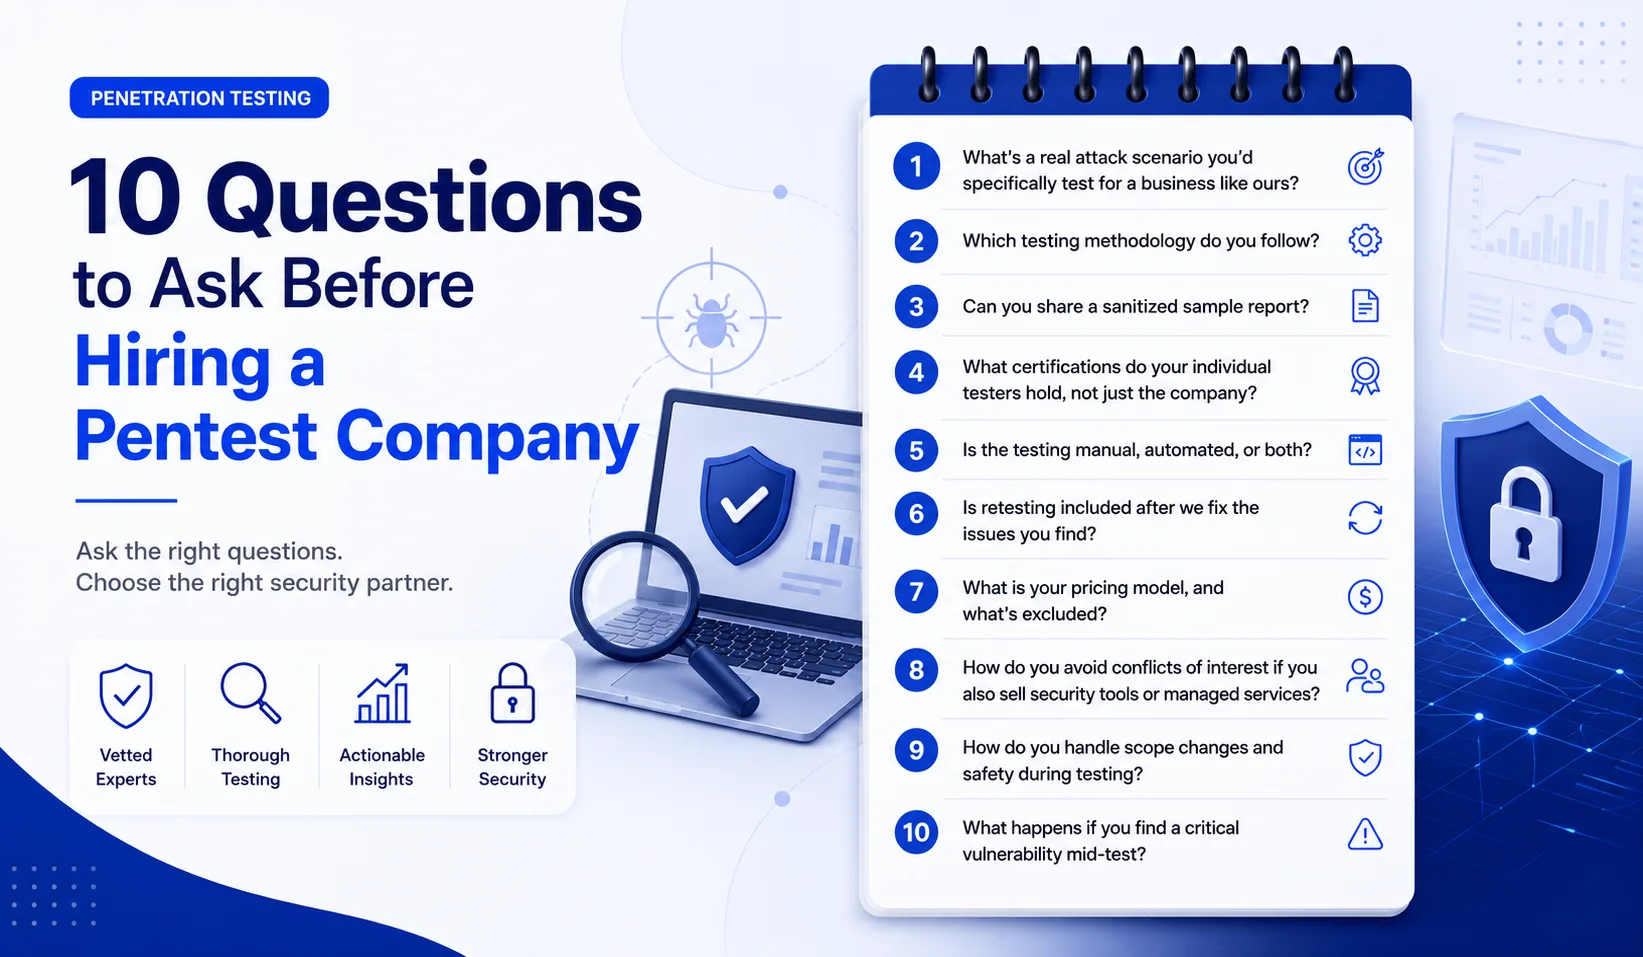
Most penetration testing quotes look identical on paper: a scope, a timeline, a price. The difference between a vendor who finds the vulnerability a real attacker would use and one who hands you a scanner printout with a logo on it only shows up in how they answer questions before you sign anything. Three questions […]