Posted on September 21st, 2026 by Cyber
The Essential 8 maturity levels measure how well an organisation has implemented the Australian Cyber Security Centre’s eight mitigation strategies, ranked from ML0 (not yet implemented) to ML3 (fully mature against sophisticated adversaries). Most Australian government contracts and critical infrastructure obligations require at least ML1, with ML2 and ML3 expected as risk and regulatory exposure […]
Posted on September 21st, 2026 by Cyber
Quick Answer Auditors generally accept vulnerability scanning as evidence of routine detection controls, but only penetration testing satisfies requirements for validated, exploit based assurance. ISO 27001, SOC 2, PCI DSS, and the ACSC Essential Eight each expect scanning on a continuous or quarterly cadence, with penetration testing performed at least annually or after significant system […]
Posted on September 21st, 2026 by Cyber
Quick Answer Yes. If you send customer data to an AI API such as OpenAI, Anthropic, or a third-party AI feature embedded in a SaaS tool, that provider is a subservice organisation and falls inside your SOC 2 scope. Auditors expect you to identify every AI vendor touching in-scope data, document the nature of that […]
Posted on September 14th, 2026 by Cyber
Quick Answer Most Australian businesses need VAPT (vulnerability assessment and penetration testing), not red teaming. VAPT finds and lists vulnerabilities across your systems on a fixed scope and timeline. Red teaming tests whether your people, processes, and detection capability can catch a realistic, multi-stage attack, and only delivers value once you already have basic security […]
Posted on September 14th, 2026 by Cyber
Quick answer The right ISO 27001 consultant will name your lead auditor, give you a written scope and timeline before any payment, and stay involved through post-certification surveillance audits. If they cannot answer these three points clearly, keep looking. The 10 questions and red flags below cover everything else worth checking before you sign. Choosing […]
Posted on September 14th, 2026 by Cyber
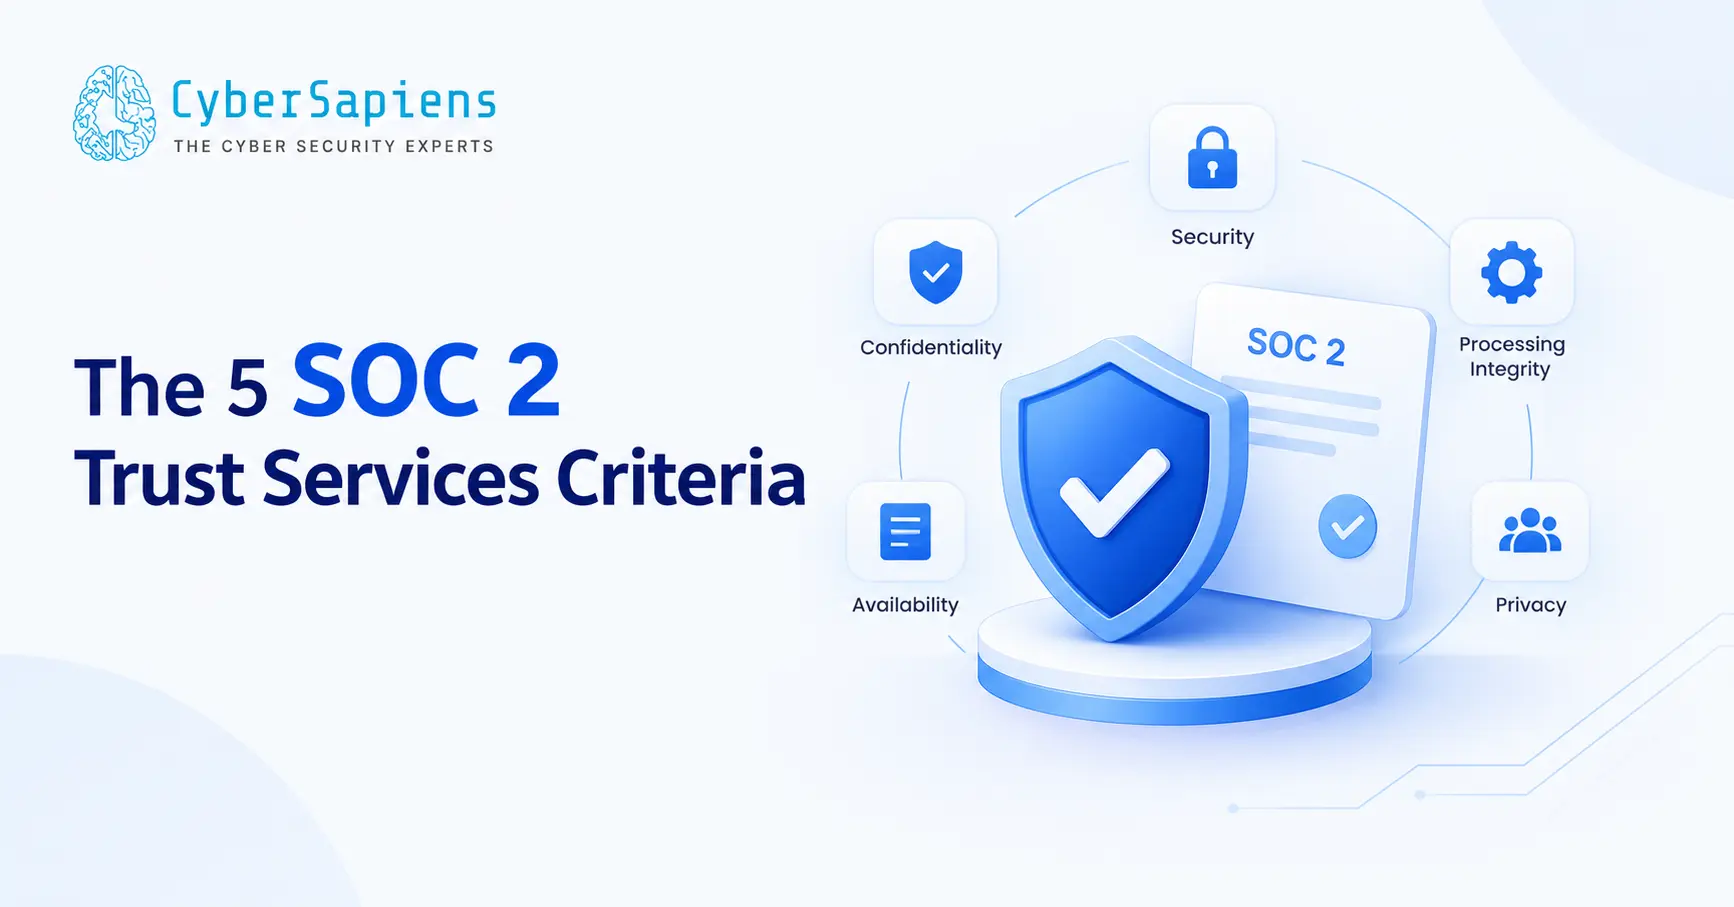
the 5 SOC 2 trust service critera
Posted on July 27th, 2026 by Cyber
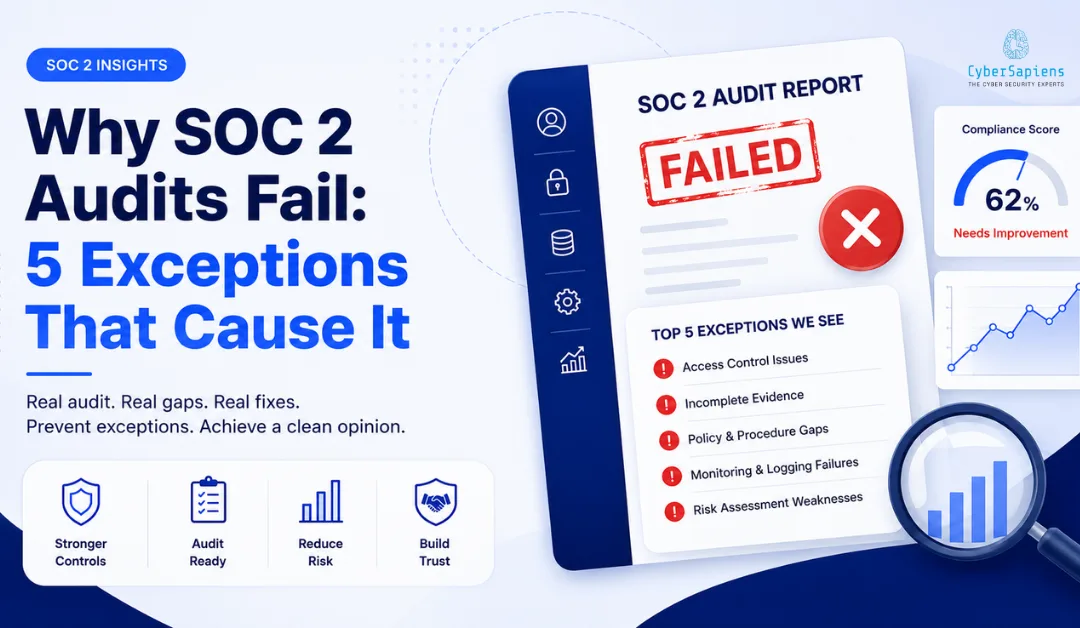
A SOC 2 audit rarely “fails” outright, true adverse opinions are uncommon. What organizations encounter far more often is a qualified opinion, where auditors identify one or more control exceptions significant enough to be documented in the final report. The five most common causes include weak access controls, missing evidence following operational changes, inadequate vendor […]
Posted on June 11th, 2026 by Cyber
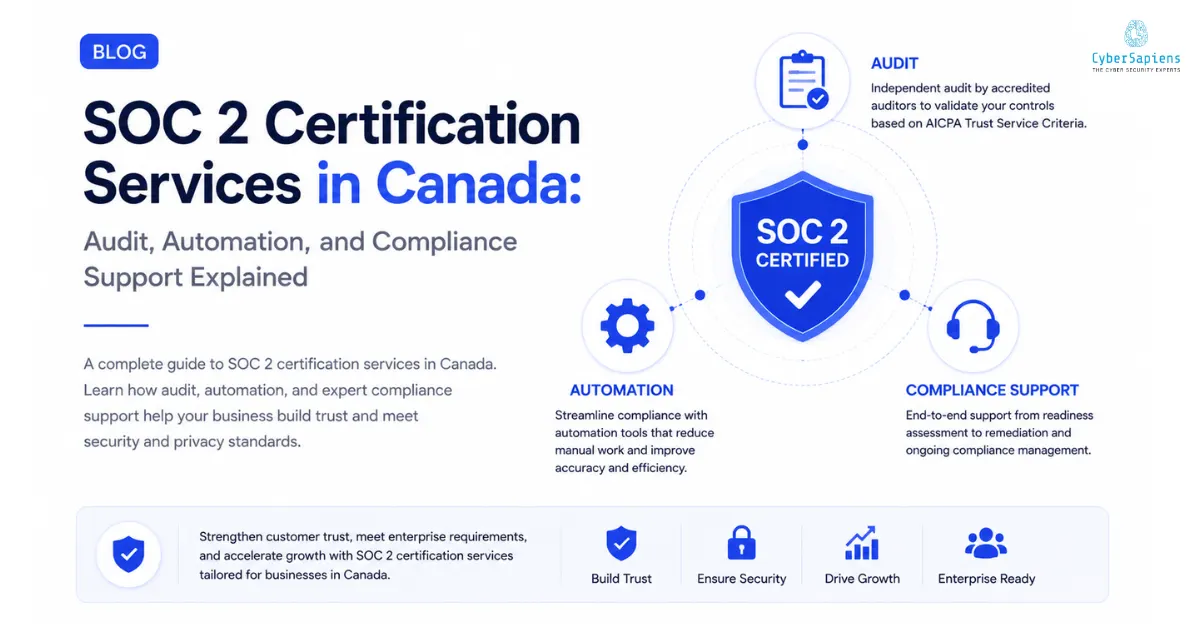
SOC 2 COMPLIANCE CANADA UPDATED 2026 SOC 2 certification services in Canada help SaaS, cloud, and technology companies prepare for, pass, and maintain a SOC 2 attestation issued by a licensed CPA firm. These services typically cover readiness assessment, gap remediation, evidence preparation, audit coordination, and ongoing compliance support after the report is issued. For […]
Posted on May 11th, 2026 by Cyber
AUSTRALIAN SAAS COMPLIANCE GUIDE For most Australian SaaS companies, SOC 2 Type 1 readiness typically takes several weeks of preparation, while SOC 2 Type 2 certification requires a longer observation period with continuous evidence collection and operational maturity. The exact timeline depends on infrastructure complexity, security maturity, customer requirements, and internal compliance ownership. This guide […]
Posted on April 17th, 2026 by Cyber
SOC2 compliance vendors in India help SaaS, fintech, and tech firms secure Type 1/2 certification, reduce breach risks, and build enterprise trust. With global clients demanding SOC 2 reports, expert vendors manage readiness, audits, controls, and renewals efficiently. Key selection factors: local expertise, full-service support, scope alignment. Costs vary by company size, evidence needs, and […]