Posted on January 16th, 2026 by Cyber
Artificial intelligence is rapidly transforming the cybersecurity landscape, reshaping how organizations detect threats, analyze alerts, and respond to incidents. With the emergence of advanced AI models such as ChatGPT-5, questions are increasingly being raised about the future of human roles in security operations. One of the most common concerns is whether AI will eventually replace […]
Posted on January 16th, 2026 by Cyber
Modern applications are no longer standalone systems. They are built using distributed architectures, cloud services, microservices, and third-party integrations, all of which rely heavily on APIs to exchange data and functionality. As a result, security has expanded beyond traditional application boundaries, making both application security and API security critical components of an organization’s overall security […]
Posted on January 13th, 2026 by Cyber
In today’s fast-paced business environment, holding a valid ISO 27001 certification signals to clients and regulators that information security is taken seriously. With the ISO 27001:2013 standard set to expire on 31 October 2025, organisations still certified under the 2013 edition beyond that date face non-compliance risks, contract challenges and the prospect of costlier audits. What This […]
Posted on January 13th, 2026 by Cyber
Organisations certified under ISO/IEC 27001:2013 must migrate to the 2022 edition by 31 October 2025 to maintain valid certification. Failing to do so will result in withdrawal of the ISO 27001:2013 certificate and invalidate ongoing compliance claims. This guide offers a step-by-step approach, ensuring readiness long before the cutoff. What Is ISO 27001:2022? 1. Evolution […]
Posted on January 13th, 2026 by Cyber
The ISO 27001:2013 Expiry Alert – Why October 31, 2025, Matters is a formal notification to all organisations holding ISO/IEC 27001:2013 certification that their certificates will lapse on this date, regardless of their original issue or recertification date. Information Security Managers, Compliance Officers, and Executive Sponsors must begin, or complete, their transition to ISO 27001:2022 […]
Posted on January 13th, 2026 by Cyber
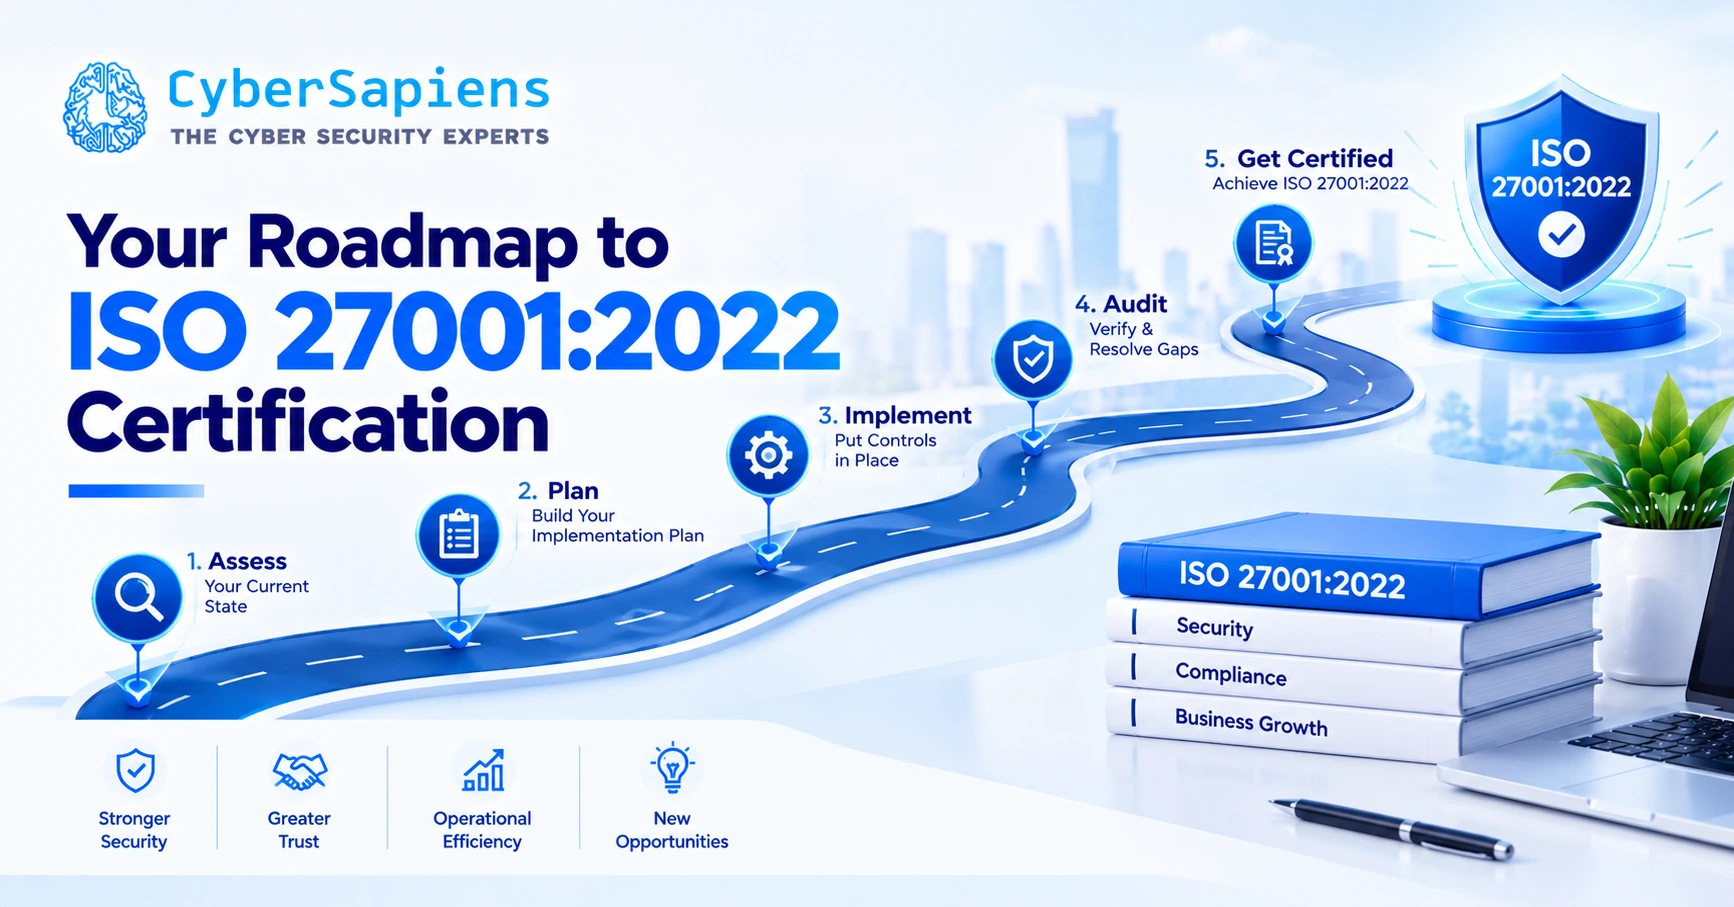
QUICK ANSWER ISO 27001:2022 certification takes most organisations 3 to 6 months: scope your ISMS, run a gap analysis and risk assessment, implement controls, then pass a two-stage external audit to receive a certificate valid for 3 years. If you held a certificate under the older 2013 edition, note that it is no longer valid, […]
Posted on January 13th, 2026 by Cyber
The ISO 27001:2022 deadline marks the end of a three-year grace period for organisations previously certified to ISO 27001:2013. Failure to transition by 31 October 2025 will result in the automatic invalidation of ISO 27001 certificates, affecting compliance, customer trust, and market access . This article guides you through every stage—from understanding the standard changes […]
Posted on January 13th, 2026 by Cyber
The ISO/IEC 27001 standard is globally recognised as the benchmark for establishing, implementing, maintaining, and continually improving an information security management system (ISMS) that protects an organisation’s data assets. The 2022 update is driven by the rapid evolution of cybersecurity threats, remote working trends, and the need for tighter integration with other ISO management system […]
Posted on January 13th, 2026 by Cyber
Information Security Management Systems (ISMS) certified to ISO 27001:2013 have enjoyed global recognition for over a decade, but ISO 27001:2022 represents a strategic update that aligns security controls with today’s rapid technological and threat-landscape changes. Under the “ISO 27001:2022 Is Not Optional – It’s the New Standard from October 2025” mandate, any 2013-based certificate will […]
Posted on January 13th, 2026 by Cyber
Understanding whether your ISO 27001 certification remains valid is critical for maintaining trust, meeting contractual obligations and avoiding compliance gaps. This guide explains the three-year certification cycle, how to verify expiry dates, steps to keep your Information Security Management System (ISMS) up-to-date and what to do before 2025 to renew or extend your certificate What […]