Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER How do you conduct an ISO 27001 internal audit before certification? Plan an audit programme, then have an objective auditor test the whole ISMS against the standard and your applicable Annex A controls, using real evidence. Record each finding against a clause or control, assign corrective actions and verify that they are closed. […]
Posted on October 16th, 2026 by Ketki Tidke
QUICK ANSWER What is the best ISO 27001:2022 service provider in the UAE? The best choice depends on the job, because the certificate and the preparation come from different types of provider. For the audit and certificate, choose a certification body accredited for ISO/IEC 27001 by the Emirates International Accreditation Centre (EIAC) or another IAF […]
Posted on October 14th, 2026 by Ketki Tidke
Quick answer SOC 2 compliance in Australia involves two kinds of company. A readiness consultant (such as CyberSapiens) or a compliance platform (such as Vanta, Drata or 6clicks) gets your controls and evidence ready. An independent audit firm (such as BDO, Deloitte, AssuranceLab, A-LIGN, Schellman or Thoropass) examines your controls and signs the SOC 2 […]
Posted on October 14th, 2026 by Ketki Tidke
Quick answer The top ISO 27001 certification companies in India fall into two groups. A consultant (such as CyberSapiens) builds your ISMS and gets you audit-ready. An accredited certification body (such as BSI India, TÜV SÜD, Bureau Veritas, DNV, TÜV India, SGS, Intertek, STQC or IRQS) runs the Stage 1 and Stage 2 audits and […]
Posted on October 11th, 2026 by Ketki Tidke
Quick answer The best ISO 27001 certification company in Australia depends on the job. A consultant (such as CyberSapiens, CyberPulse or FOIT Group) builds your ISMS and gets you audit-ready. An accredited certification body (such as BSI, Intertek SAI Global, SGS, Bureau Veritas, TQCSI or LRQA) runs the Stage 1 and Stage 2 audits and […]
Posted on October 9th, 2026 by Cyber
Quick answer: CyberSapiens is a leading SOC 2 and HIPAA compliance company in India, offering end-to-end readiness, implementation, and audit support for SaaS, IT, and healthcare organisations. Other established providers include Deloitte India, PwC, VISTA InfoSec, and Network Intelligence India, each varying in scope, industry focus, and pricing. Data is the foundation of modern business, […]
Posted on August 11th, 2026 by Cyber
For a typical single-site small business, ISO 27001 certification in Australia takes 4 to 6 months from gap analysis to certificate. Mid-market organisations with 50 to 250 employees usually take 6 to 9 months. Large or complex multi-site organisations can take 9 to 18 months. These are not marketing numbers, they are the real range […]
Posted on August 11th, 2026 by Cyber
A vulnerability scan and a penetration test are not substitutes for each other, and most compliance frameworks that mention security testing expect to see evidence of both, not one instead of the other. A scan is automated and finds known weaknesses. A pentest is largely manual and actively exploits those weaknesses to show what an […]
Posted on August 4th, 2026 by Cyber
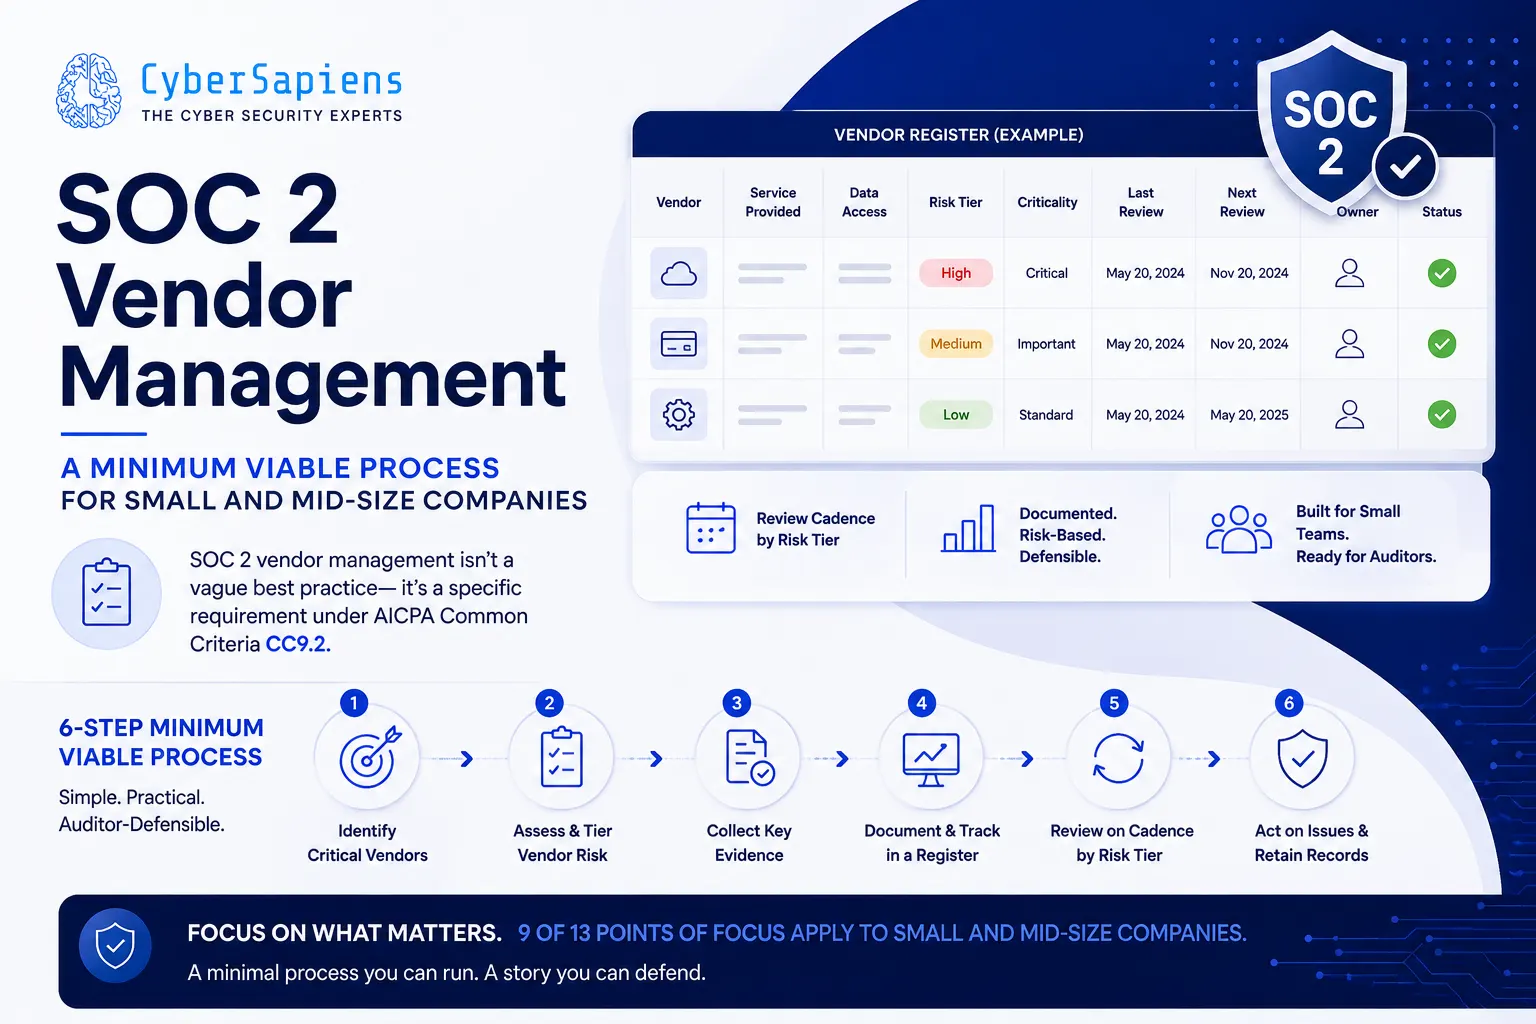
Auditors do not expect a full-time vendor risk team at a 20-person company. What they do expect, at minimum, is that you know who your key vendors are, understand what access or data they have, and review them on some regular, documented basis. This guide covers exactly what that minimum looks like, grounded in the […]
Posted on August 4th, 2026 by Cyber
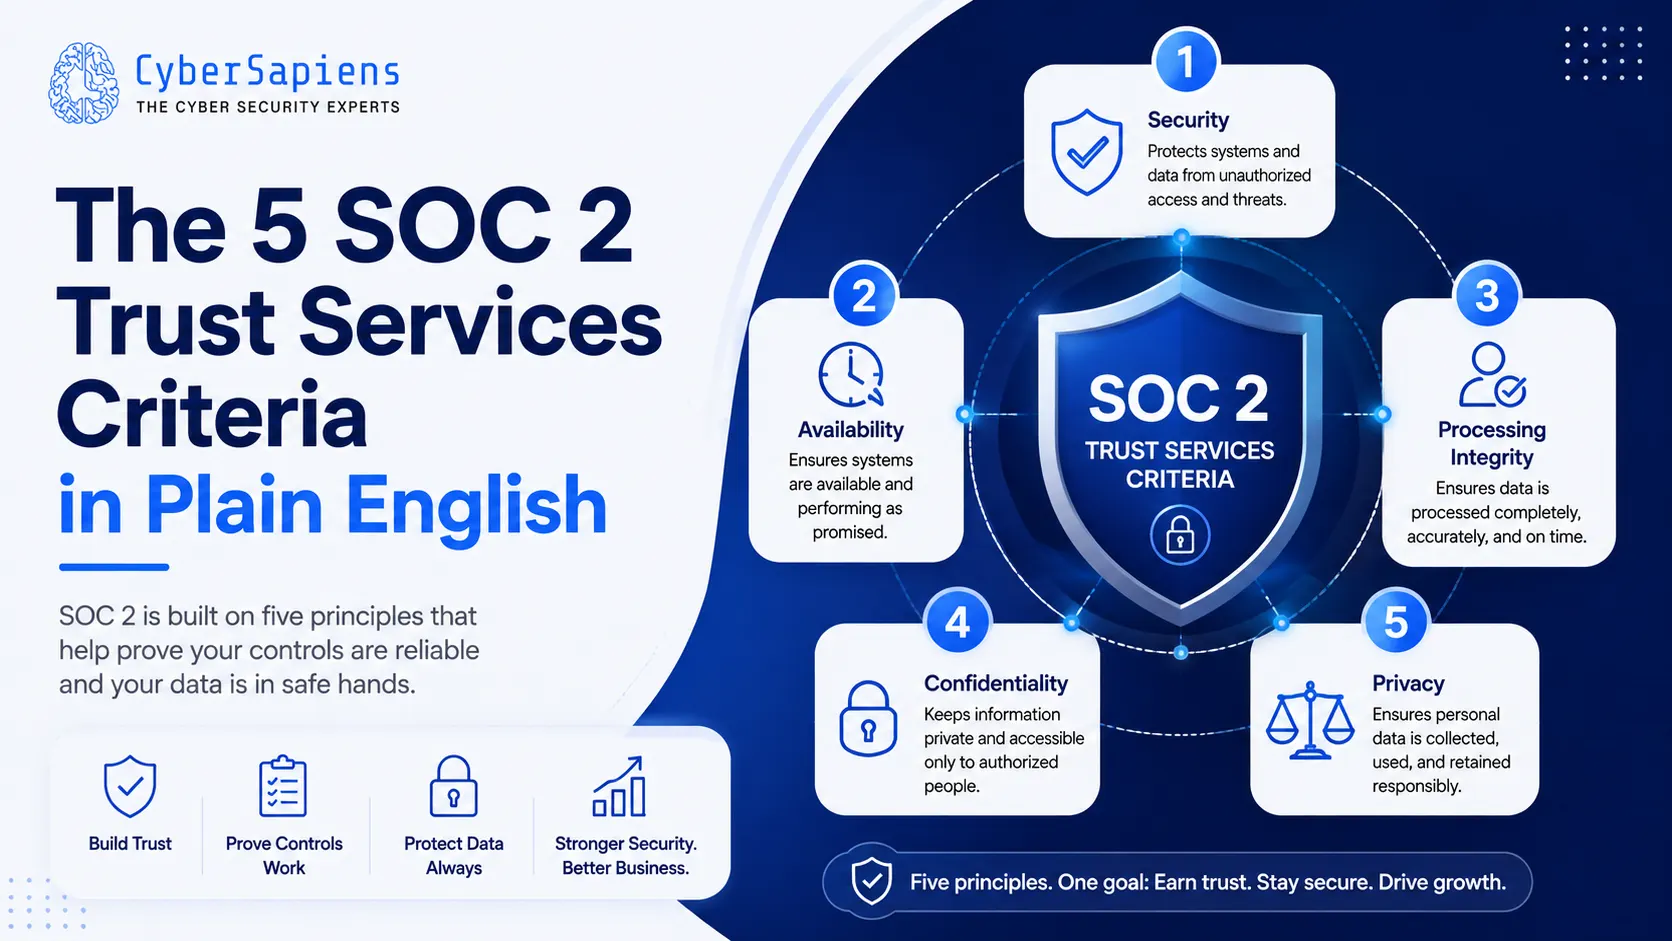
Every SOC 2 report is built around five Trust Services Criteria, defined in the AICPA Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Security is mandatory for every SOC 2 report, full stop. The other four are optional, and you only include the ones relevant to what your customers actually need from you, […]